Programmable Compliance
Smart Contracts
Governed Financial Infrastructure
SMART CONTRACTS
Conceptual Transformation Scenario
Web3 Product & Strategy Lead
Brian designed a governance architecture for evaluating smart-contract-based financial agreement execution in regulated institutional environments. The work focused on lifecycle governance, institutional authority, programmable compliance controls, escalation pathways, audit visibility, and responsibility boundaries across on-chain execution, off-chain systems, and human governance.
A Global Financial Institution examined whether smart contracts could support automated financial agreement behavior without weakening institutional authority, accountability, auditability, or control. Brian created four artifacts: a Smart Contract Governance Lifecycle, Programmable Compliance Operating Model, Execution Authority and Escalation Model, and On-Chain and Off-Chain Responsibility Framework, that clarified how programmable execution could be evaluated as governed financial infrastructure rather than autonomous code operating outside institutional oversight.
CHALLENGE
Financial institutions operate under strict regulatory, audit, and control requirements designed to preserve accountability across financial agreement execution.
Smart contracts introduced the ability to encode financial agreement behavior into programmable execution paths, including covenant enforcement, collateral monitoring, and compliance-related controls.
However, existing governance models were not designed for deterministic execution that could trigger actions based on predefined logic. This created a structural gap between institutional control frameworks and automated execution systems
The challenge was not whether smart contracts could automate rules. It was defining how programmable execution could operate inside institutional authority, regulatory accountability, audit requirements, and human intervention controls.
The opportunity was to design a governance architecture that helped leadership evaluate programmable compliance before deployment feasibility was considered.
Key Drivers
- Lack of lifecycle governance for smart contract deployment, monitoring, upgrade, and retirement.
- Absence of defined authority delegation and escalation pathways.
- Unclear responsibility boundaries between automated execution and human oversight.
- Regulatory and audit requirements for institutional accountability and control.
- Need to automate compliance-related execution without weakening governance integrity.
- Need to align programmable execution with existing institutional control frameworks.
Strategic Question
How could a global financial institution evaluate smart contracts as programmable compliance infrastructure while preserving lifecycle governance, institutional authority, escalation controls, audit visibility, and responsibility boundaries?
This required more than confirming that rules could be encoded into smart contracts. It required a governance model for determining who could approve, activate, pause, override, escalate, change, audit, or retire programmable financial agreement behavior.
SOLUTION
The solution was a governance architecture for smart-contract-based programmable compliance, structured around lifecycle control, institutional authority, escalation and intervention rights, audit visibility, and responsibility boundaries across on-chain execution, off-chain systems, and human governance.
The solution connected four programmable compliance governance questions:
- How should programmable execution be governed across its lifecycle?
- How should programmable compliance operate inside institutional authority and control frameworks?
- Who has authority to approve, pause, escalate, intervene in, or change contract behavior?
- How should responsibility be divided across on-chain execution, off-chain systems, and human governance?
Together, these components created a governed operating model for evaluating smart-contract-based compliance execution before deployment feasibility or production implementation could be considered.
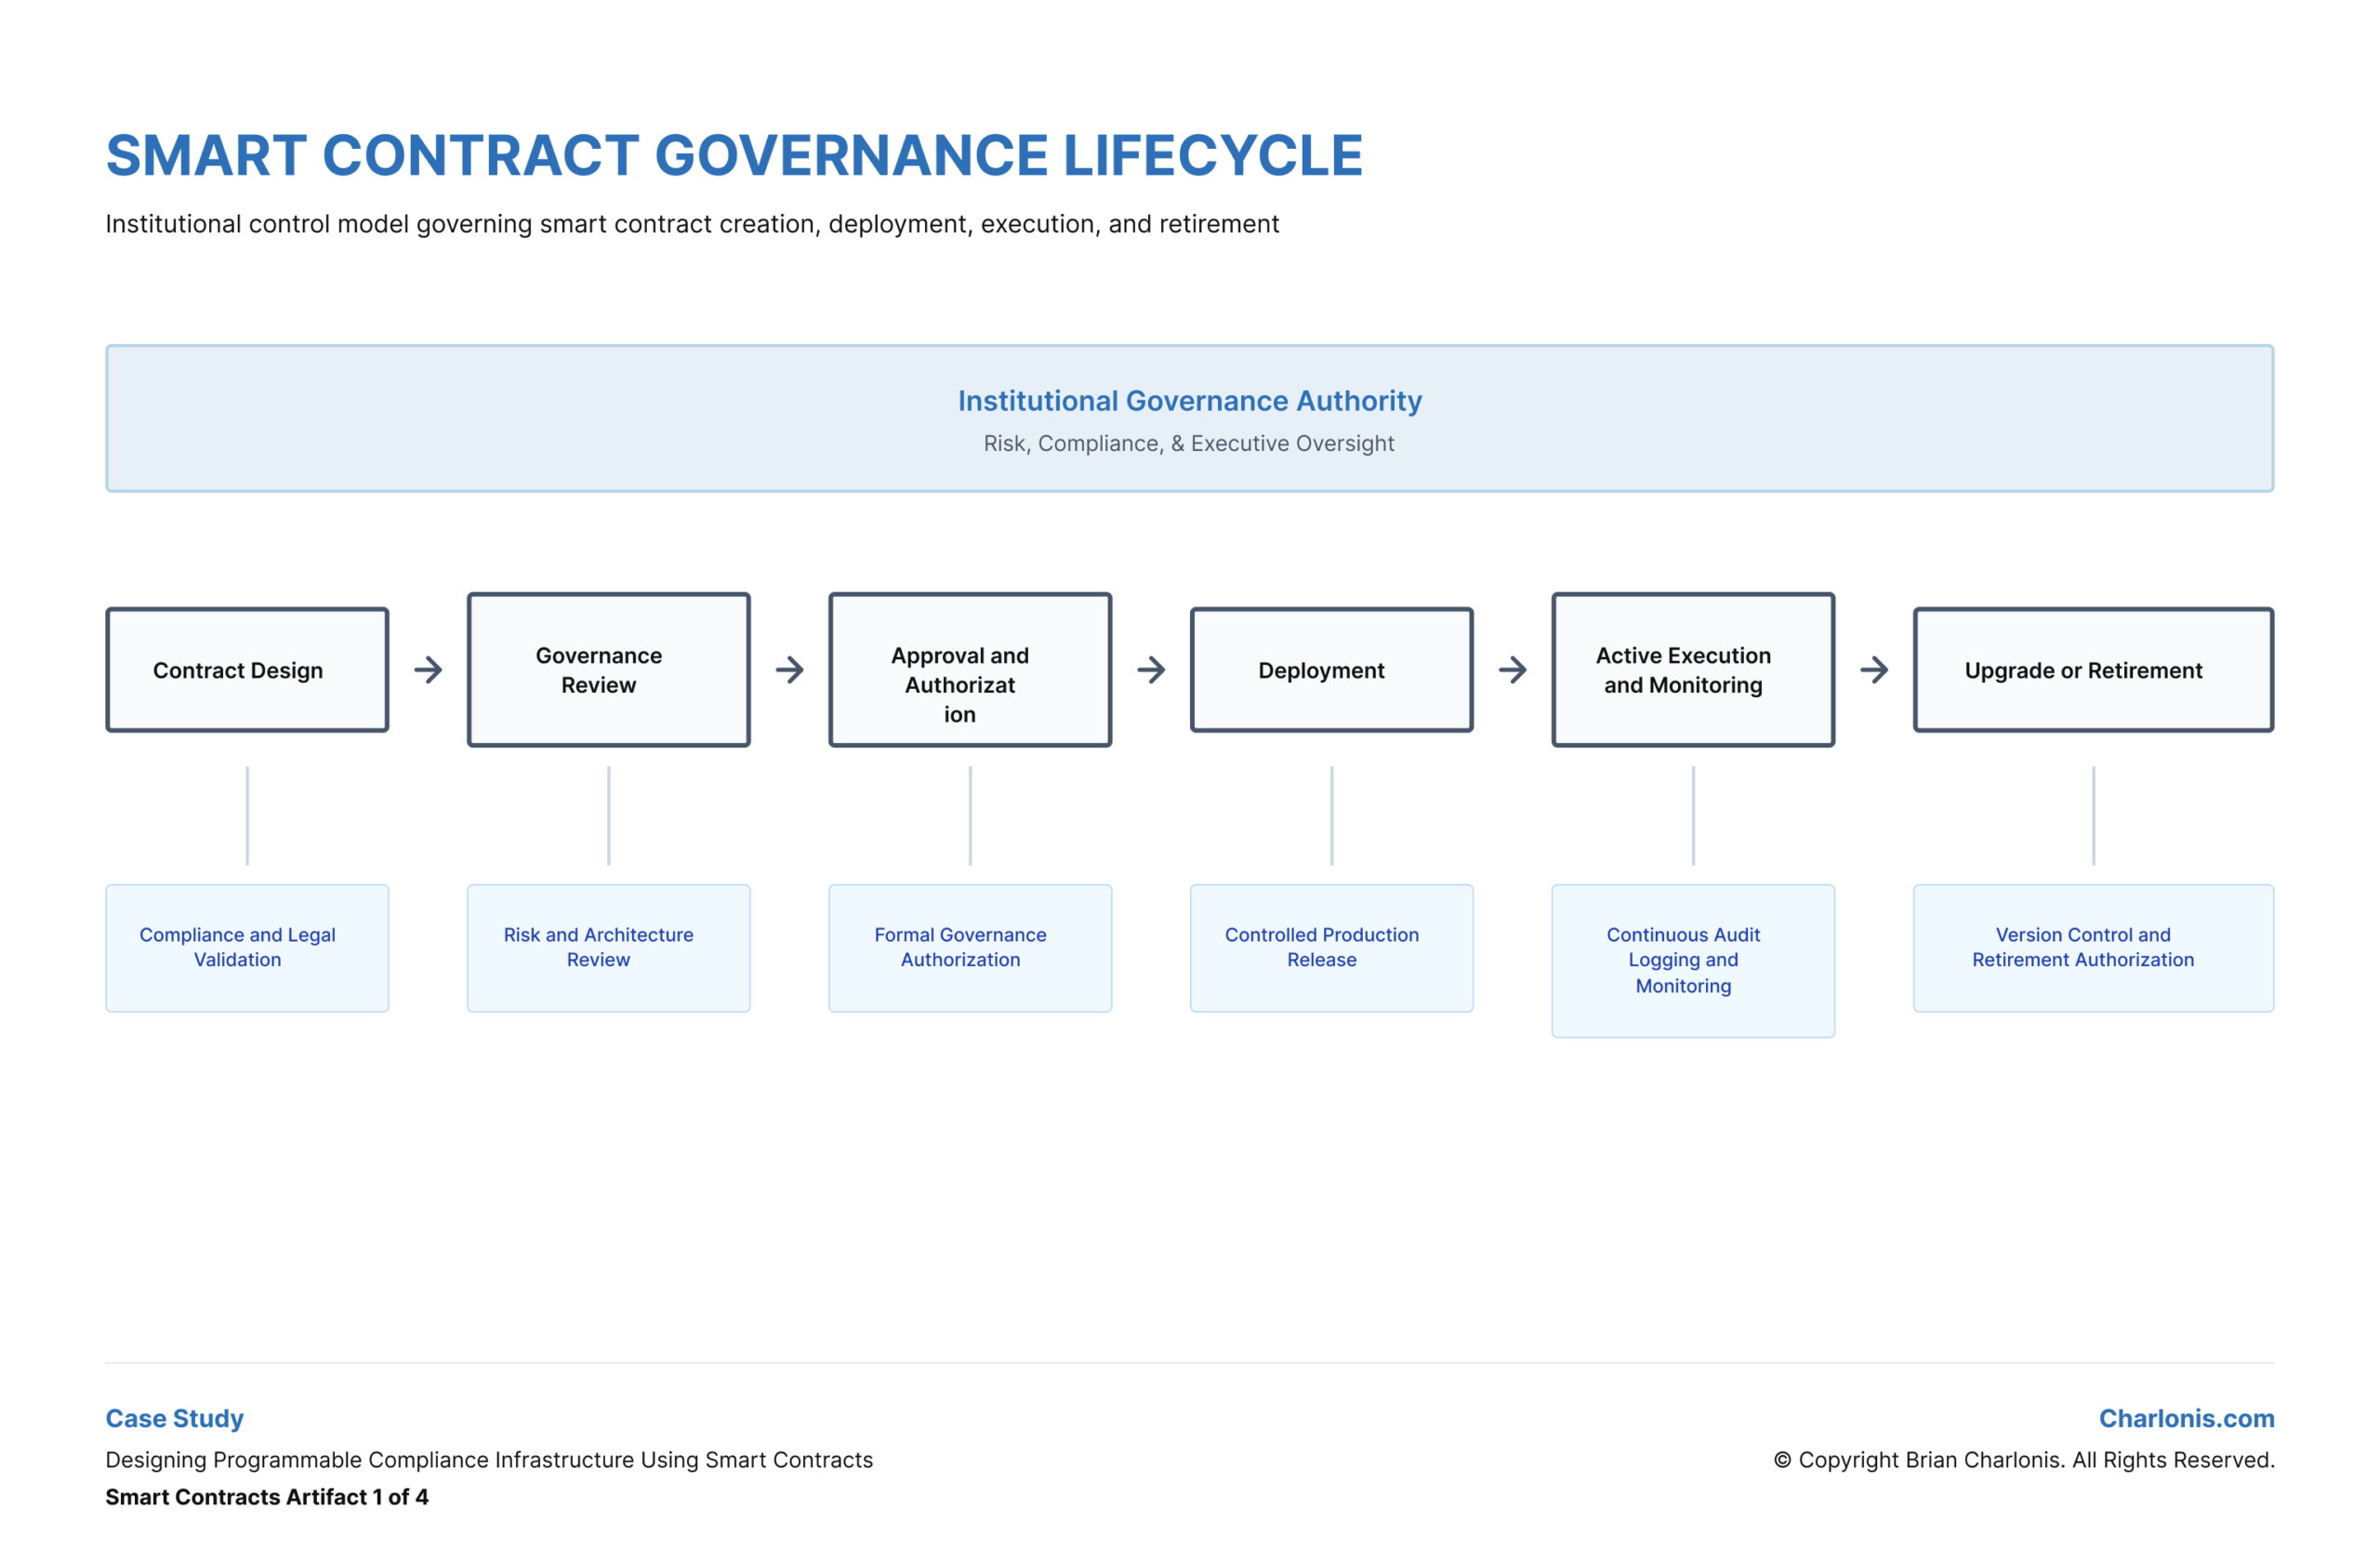
Smart Contract Governance Lifecycle
The governance lifecycle defined how programmable financial agreement behavior should move through creation, approval, deployment, execution, monitoring, upgrade, change control, retirement, and decommissioning while remaining subject to institutional governance. It clarified which checkpoints were required before smart-contract-based execution could move toward deployment consideration.
Key Elements
- Contract creation governance.
- Pre-deployment approval controls.
- Deployment authorization requirements.
- Execution monitoring expectations.
- Upgrade, change-control, retirement, and decommissioning pathways.
Artifact type: Governance lifecycle / contract-control model.
The artifact defined how programmable financial agreement behavior could move from creation through retirement while remaining subject to institutional authority, review, monitoring, and change control.
How It Shaped Decisions
This component would support governance, compliance, audit, and executive leadership stakeholders in determining which lifecycle stages required approval, how deployment readiness should be evaluated, where monitoring responsibilities should sit, and what governance conditions were required before upgrade or retirement.
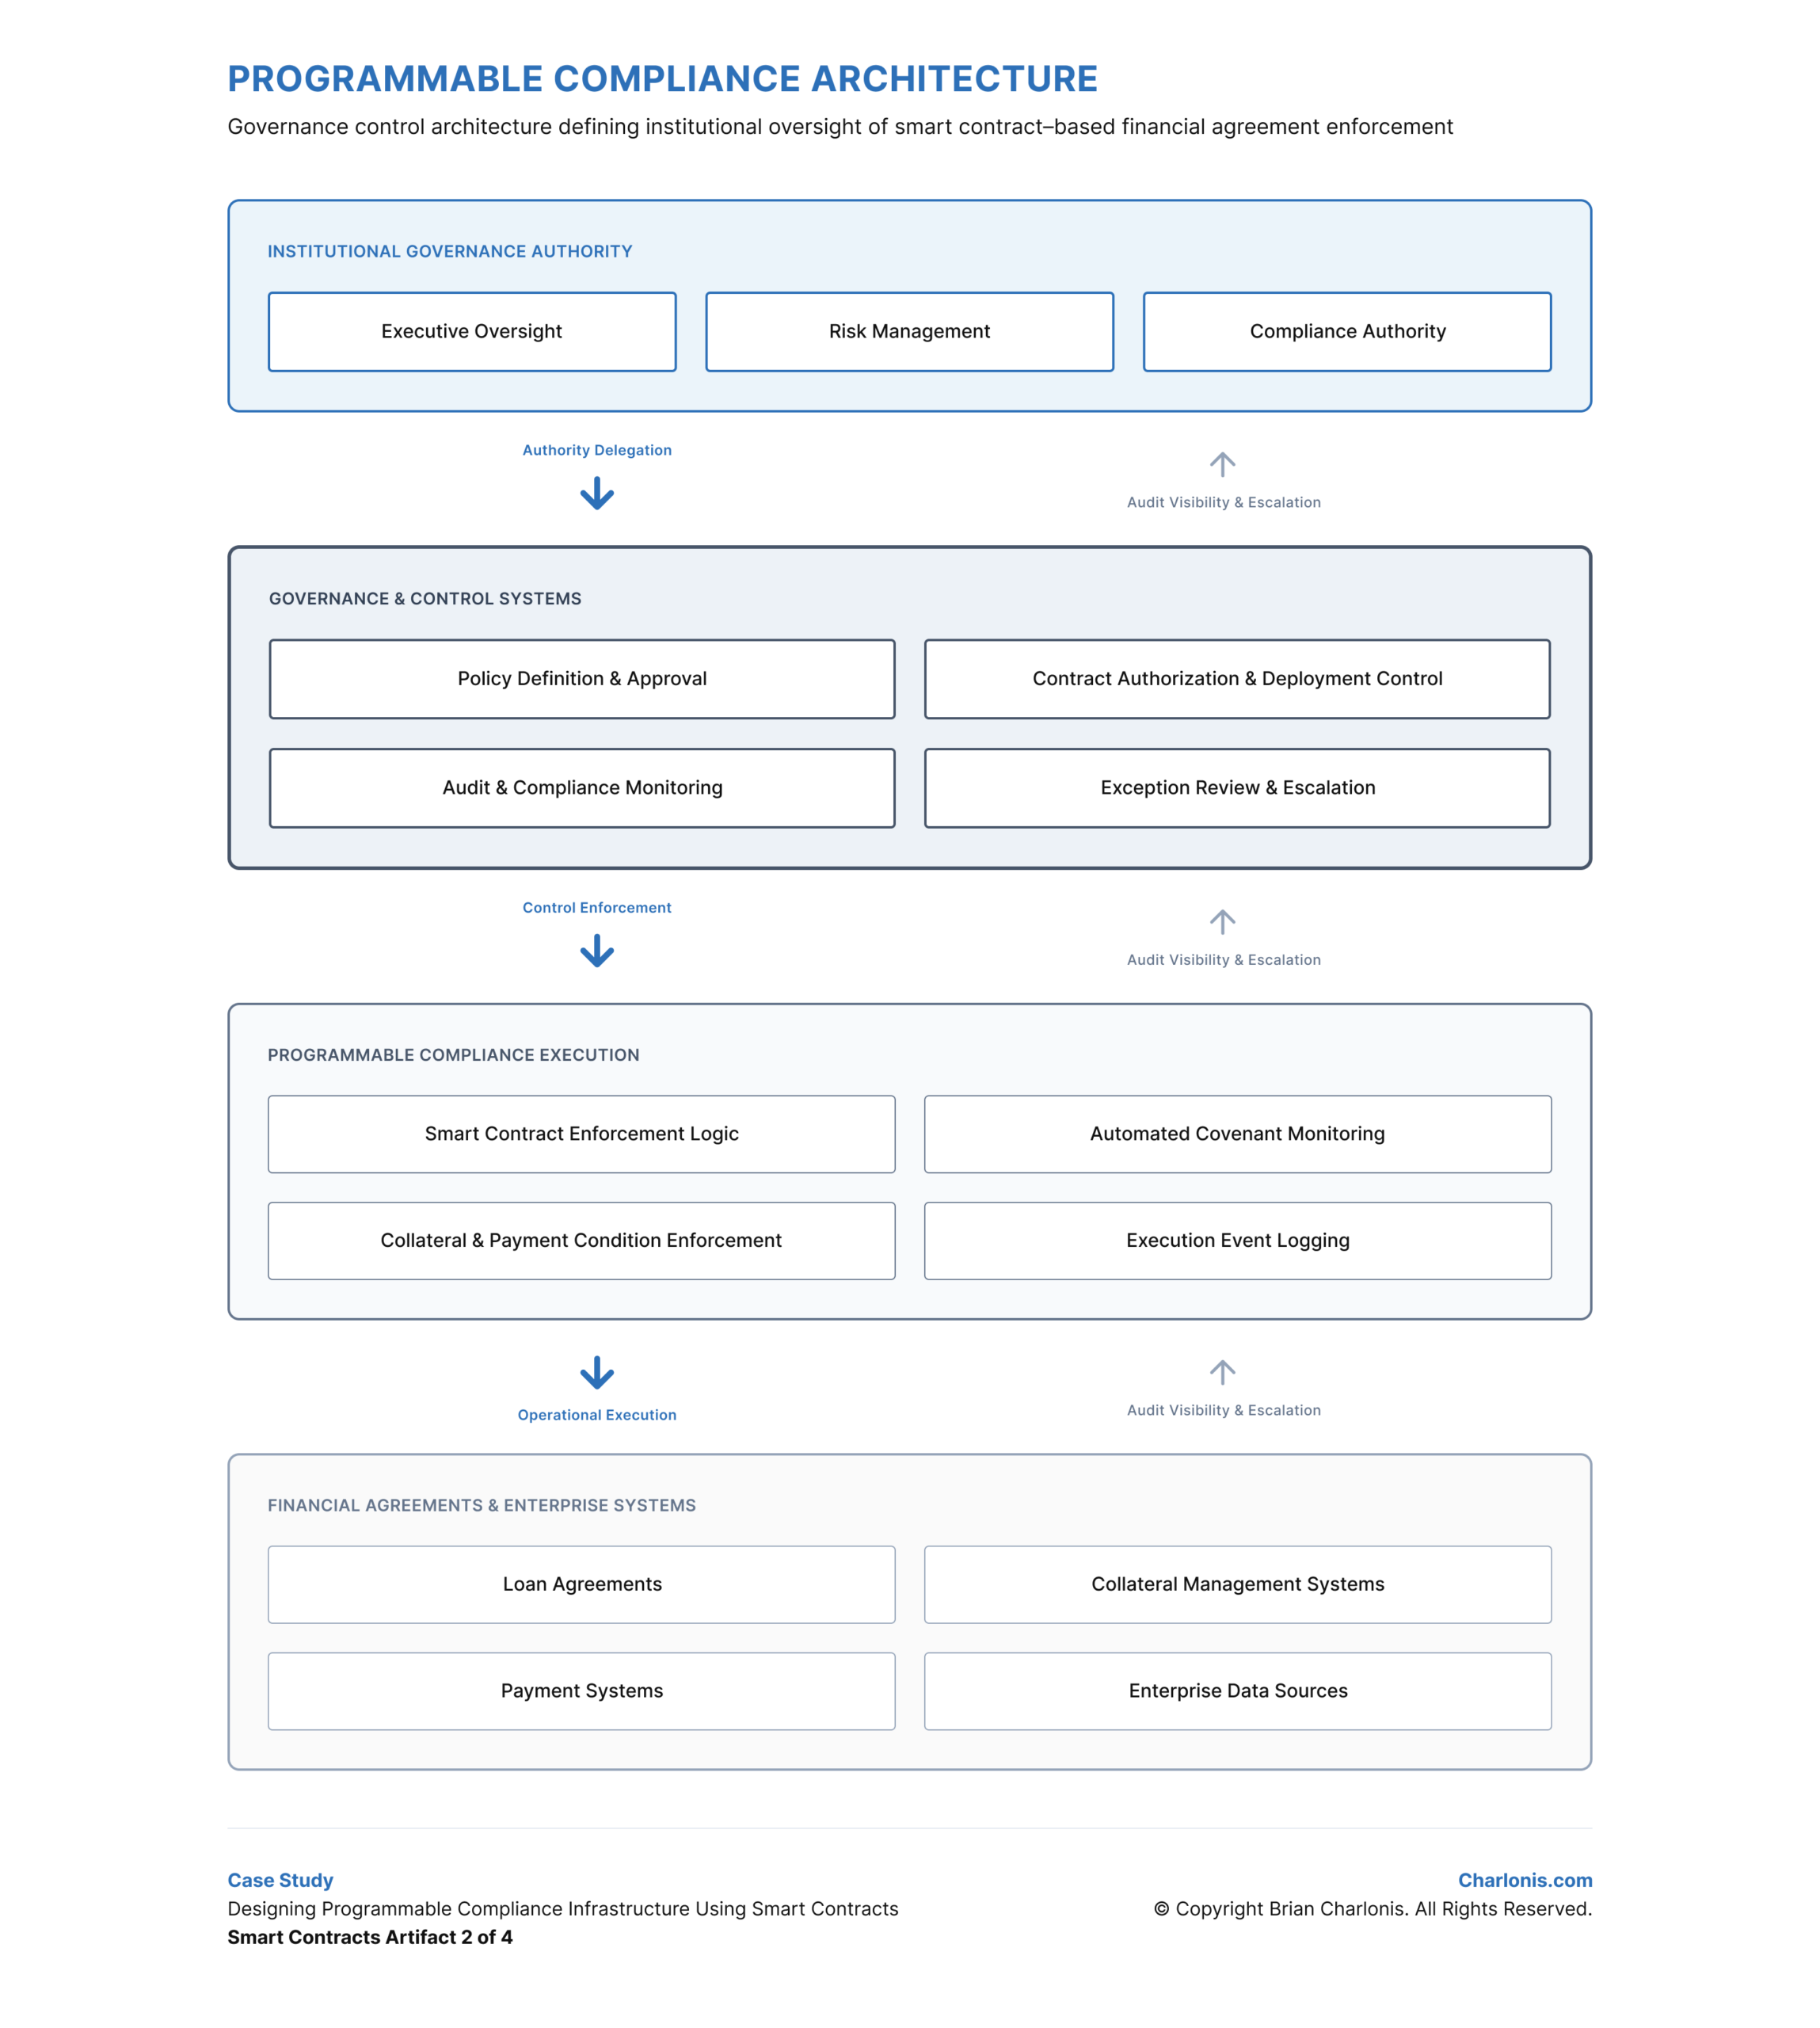
Programmable Compliance Operating Model
The operating model positioned smart contracts as programmable compliance infrastructure under institutional authority, compliance control, audit visibility, escalation pathways, and executive oversight. It clarified how deterministic execution could be evaluated without treating automation as a substitute for accountability.
Key Elements
- Layered governance architecture for programmable compliance.
- Institutional authority over automated financial agreement behavior.
- Compliance control integration.
- Audit visibility requirements.
- Escalation pathway alignment and executive oversight expectations.
Artifact type: Operating model / governance architecture.
The artifact positioned smart contracts under institutional authority, compliance control, audit visibility, and governance oversight rather than as autonomous technical systems.
How It Shaped Decisions
This component would support governance, compliance, audit, enterprise architecture, and executive leadership stakeholders in determining how programmable compliance should fit within institutional control frameworks, which oversight mechanisms were required, and how automated execution could remain accountable.
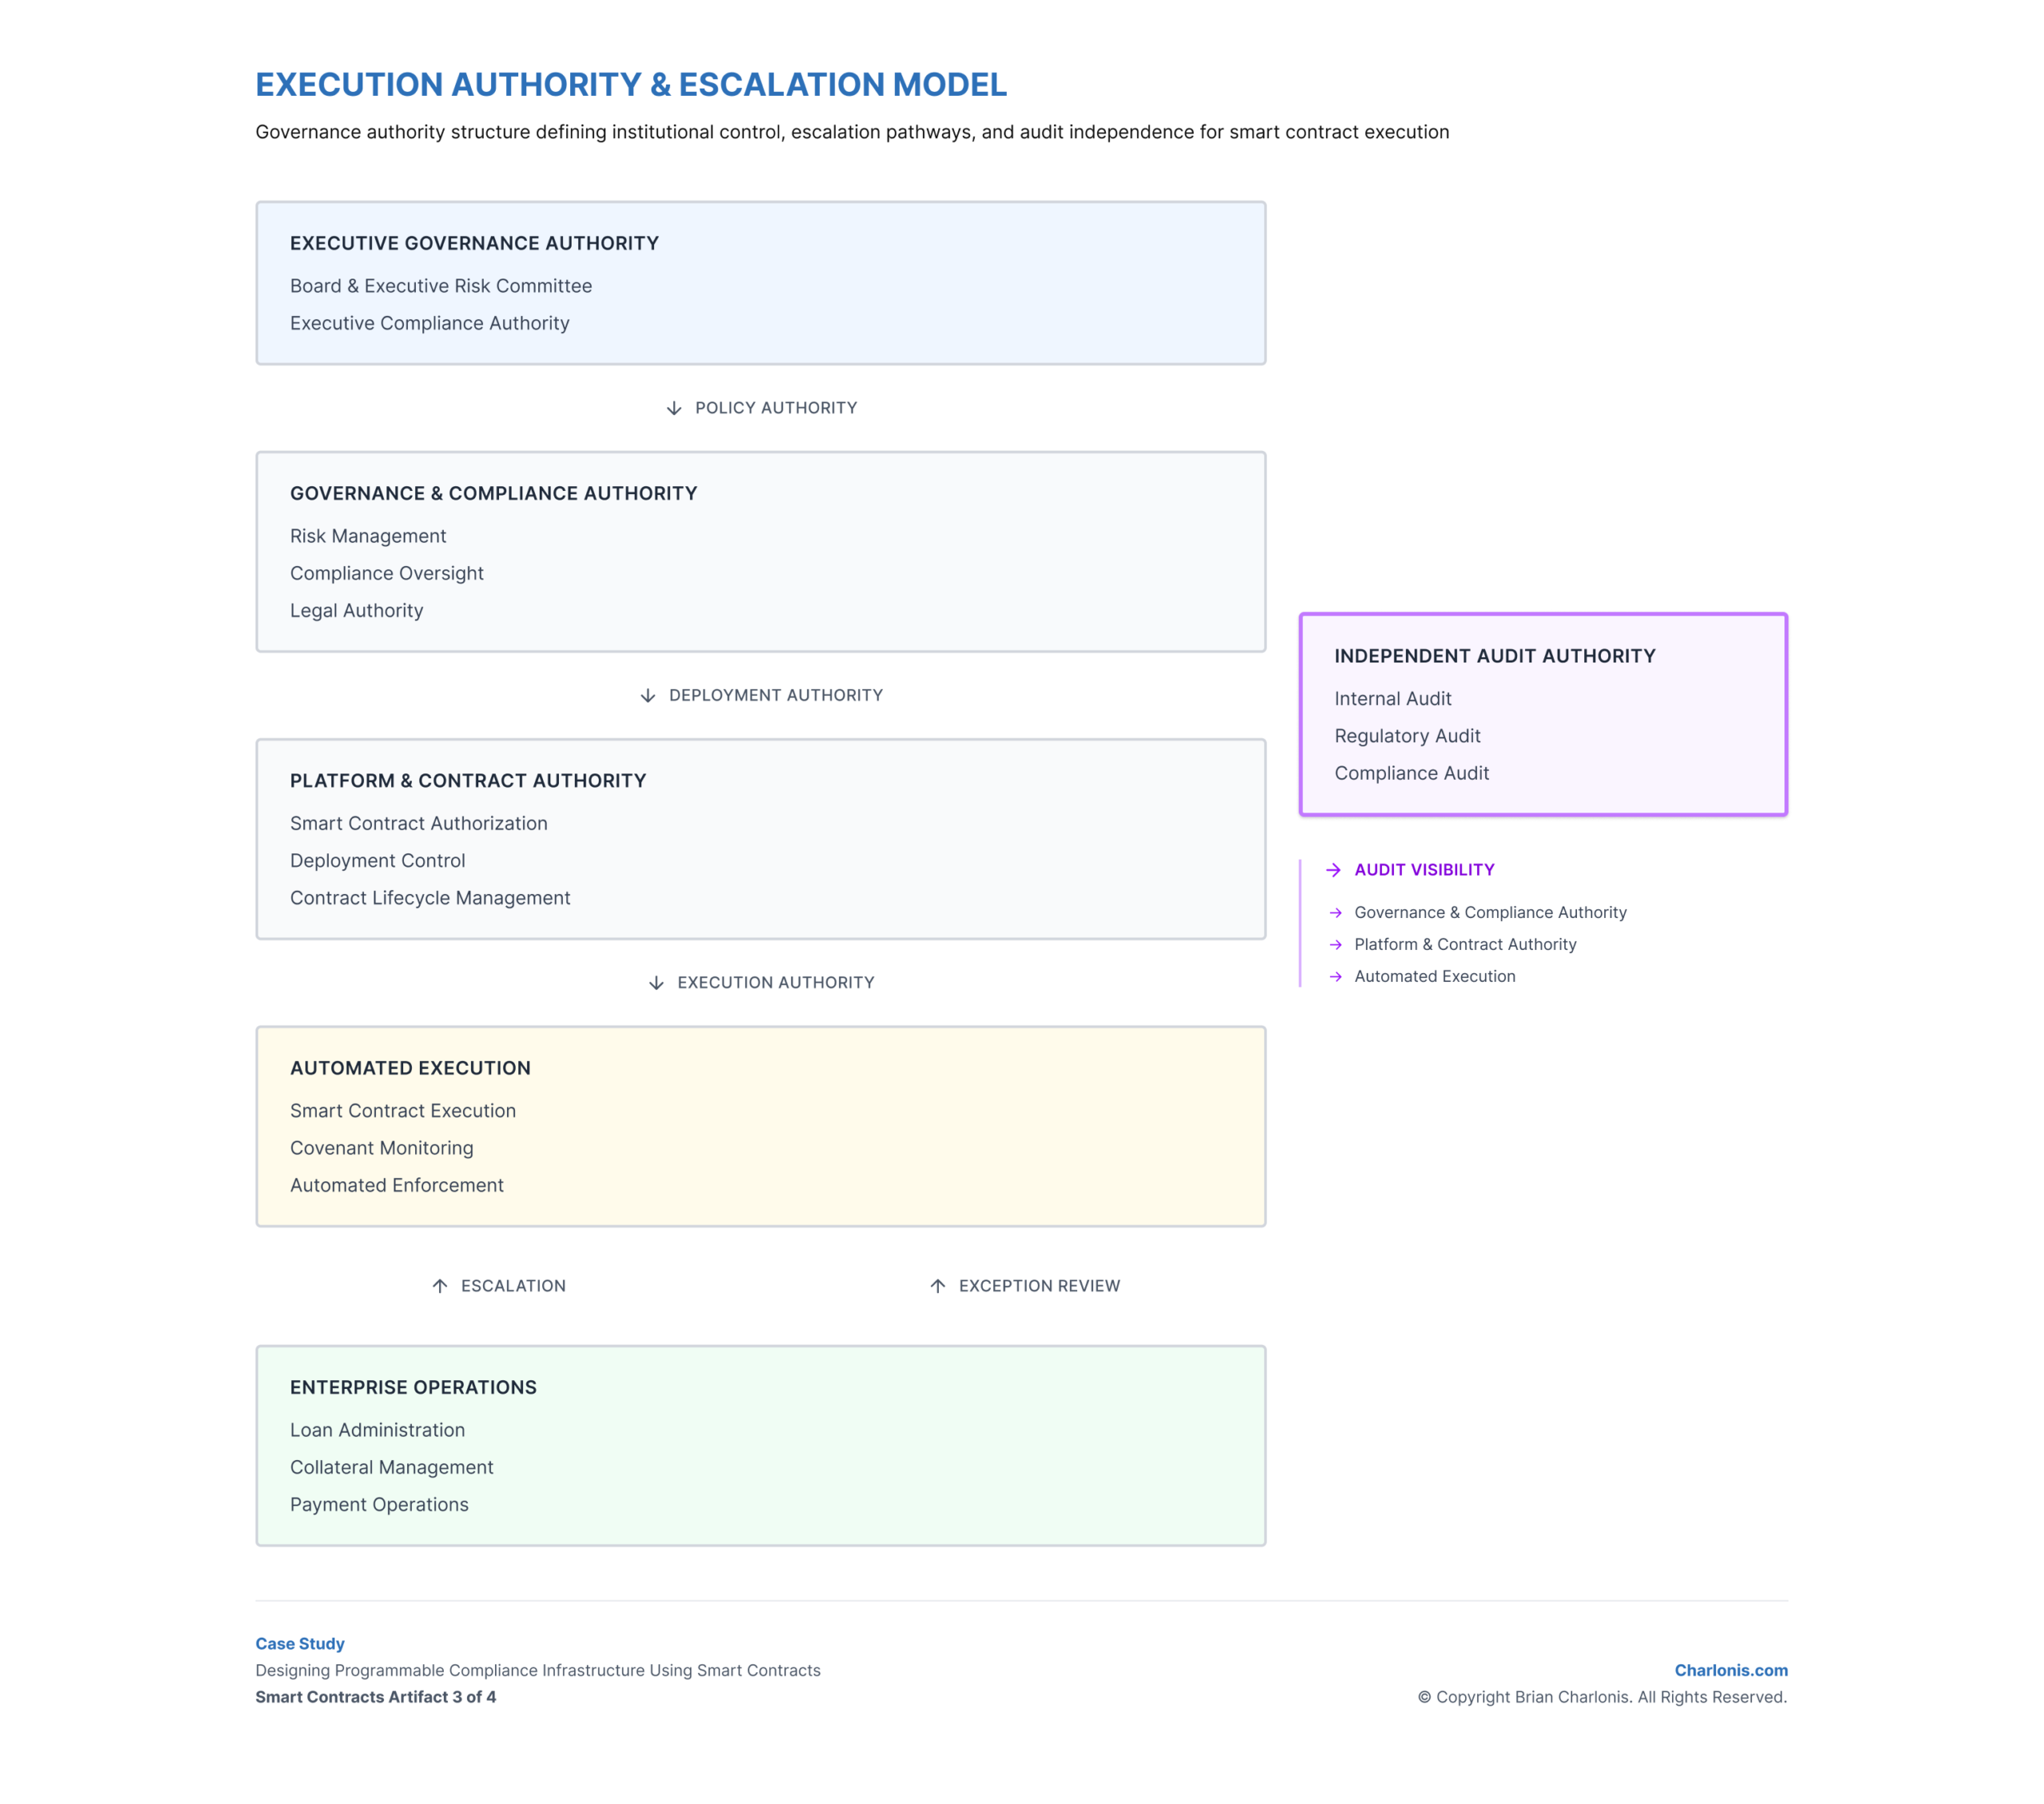
Execution Authority and Escalation Model
The authority and escalation model defined who could authorize, activate, pause, override, intervene in, escalate, or change smart-contract-based execution. It clarified that automated financial agreement behavior should not advance unless institutional intervention capability and separation of duties were defined.
Key Elements
- Authority delegation across governance and execution layers.
- Separation of duties across authorization, deployment, execution, and audit.
- Activation controls for programmable contract behavior.
- Pause, override, and intervention capability.
- Escalation pathways for exceptions, breaches, or disputed execution events.
Artifact type: Authority model / escalation framework.
The artifact connected authority delegation, separation of duties, activation controls, intervention rights, escalation pathways, and audit independence across governance and execution layers.
How It Shaped Decisions
This component would support governance, compliance, audit, platform, and enterprise architecture stakeholders in determining who could authorize contract behavior, who could activate or pause execution, how exceptions should escalate, and how separation of duties should preserve institutional control and audit independence.
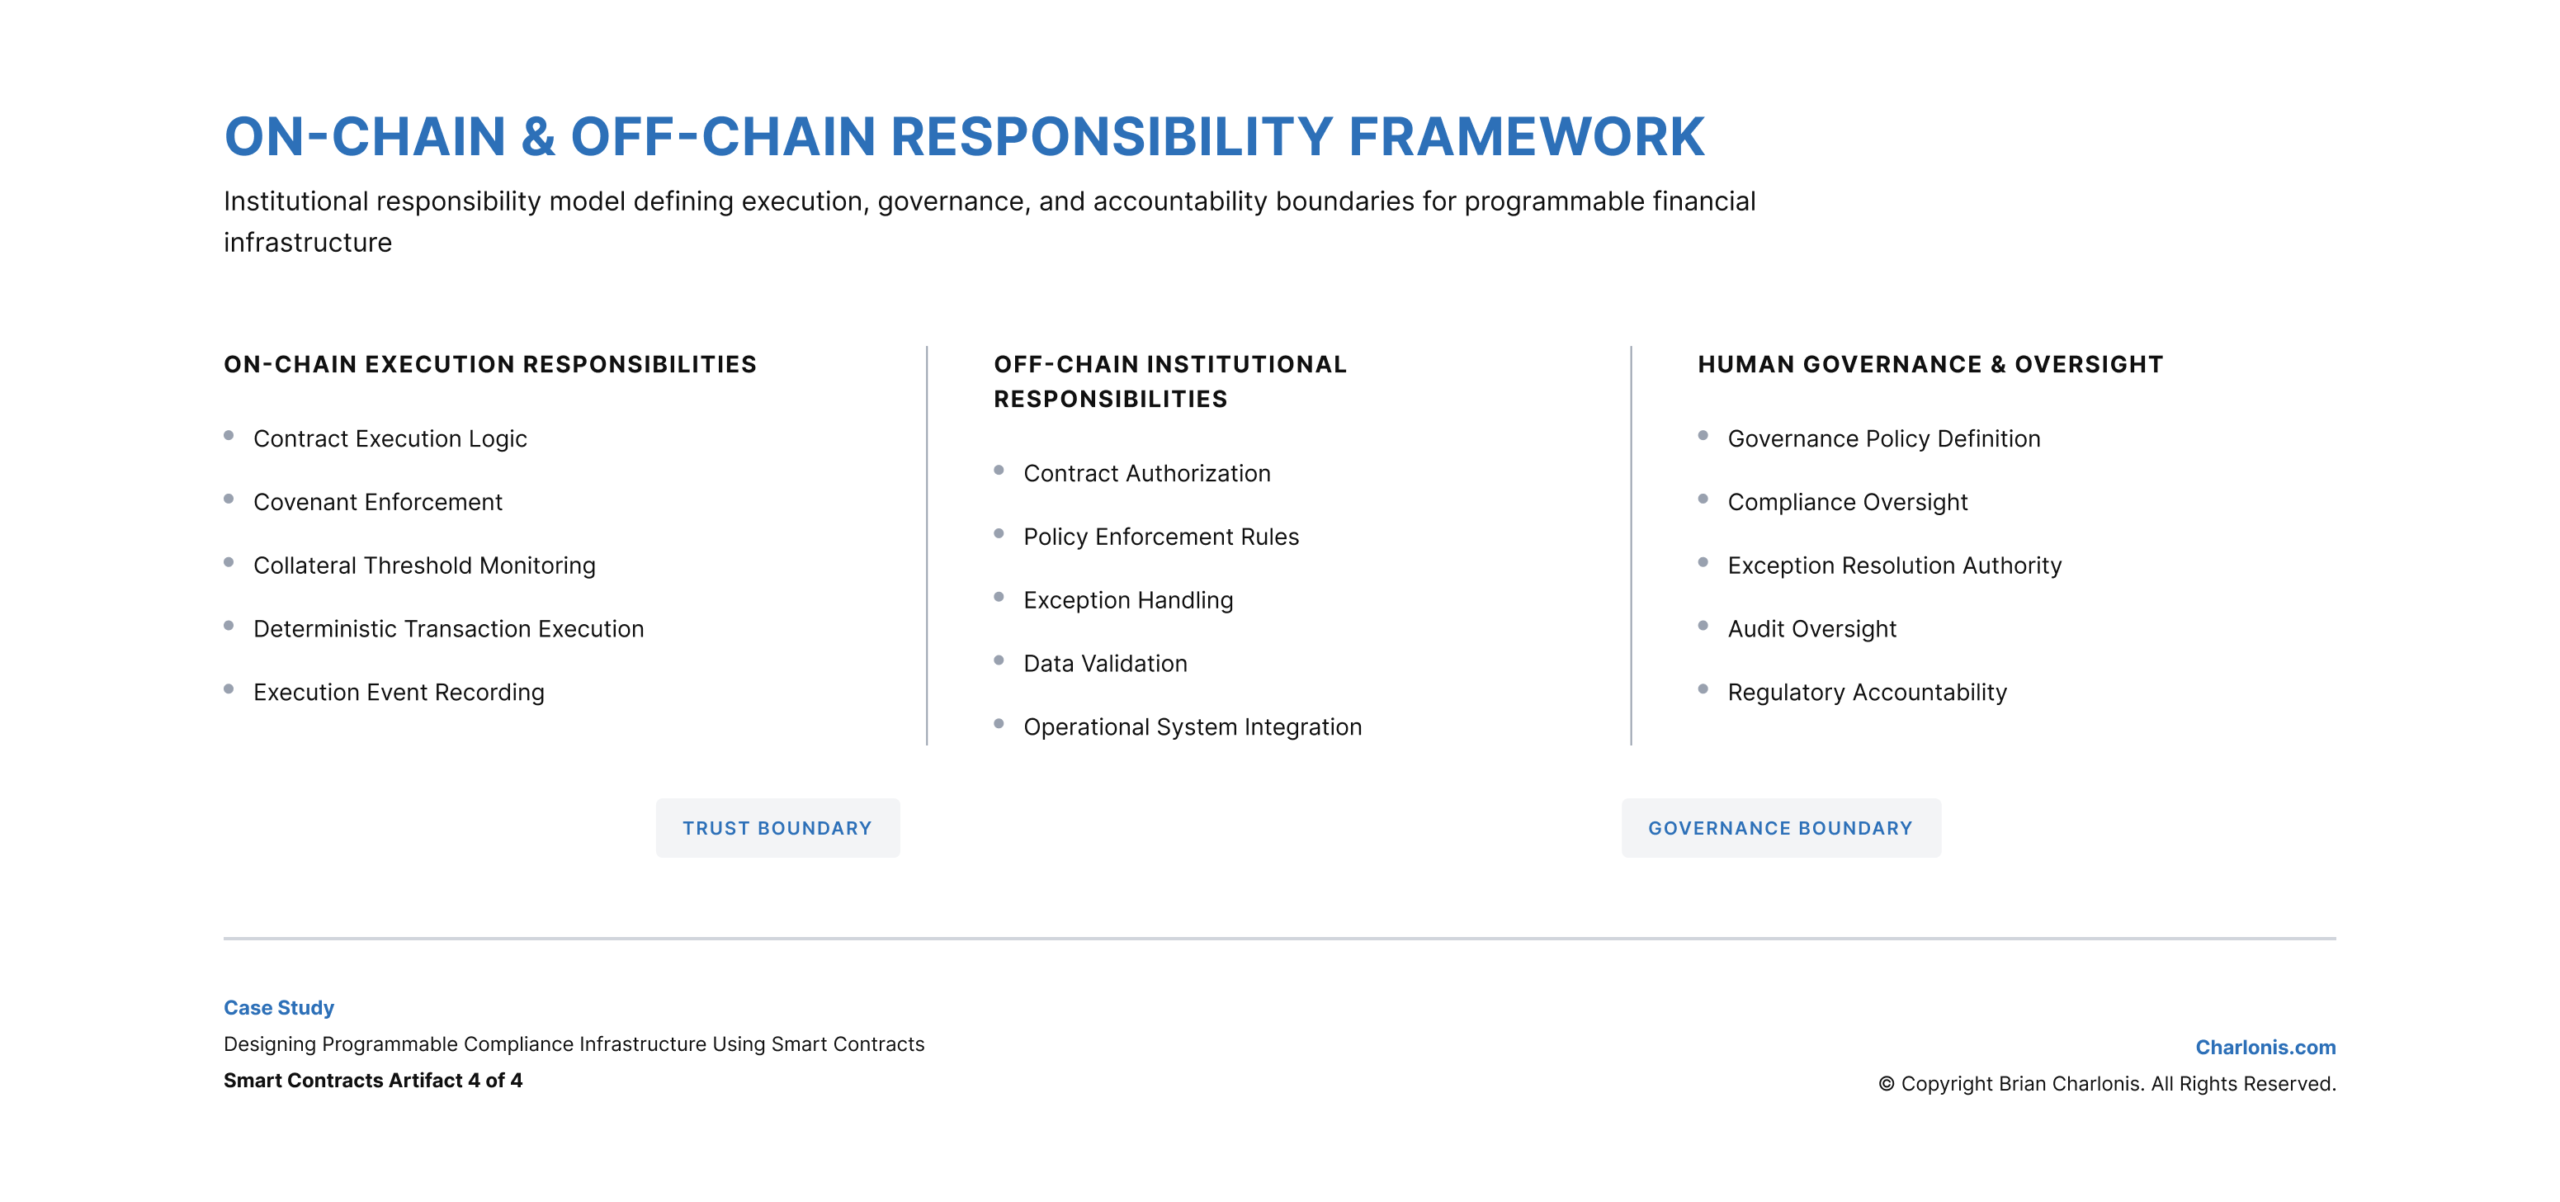
On-Chain and Off-Chain Responsibility Framework
The responsibility framework clarified accountability across programmable execution, institutional systems, off-chain data sources, and human governance. It defined which responsibilities could be supported by automated execution and which could not be delegated to code.
Key Elements
- Responsibility boundaries across on-chain execution.
- Responsibility boundaries across off-chain systems and institutional data sources.
- Human governance ownership for approval, intervention, and review.
- Accountability mapping across automated and manual control points.
- Audit evidence expectations across execution layers.
Artifact type: Responsibility framework / accountability model.
The artifact mapped accountability across programmable execution, institutional systems, human governance, audit evidence, and regulatory accountability expectations.
How It Shaped Decisions
This component would support enterprise architecture, regulatory, governance, compliance, and audit stakeholders in determining where accountability should sit across execution layers, which responsibilities could not be delegated to code, and what evidence was required to support audit, review, and regulatory accountability.
OUTCOMES
This case produced a programmable compliance governance architecture, four conceptual artifacts, lifecycle-control logic, authority-delegation model, escalation and intervention requirements, audit-visibility structure, and responsibility-boundary framework. It was developed as an independent conceptual transformation scenario and does not claim production smart-contract deployment, institutional adoption, regulatory approval, smart contract audit authority, technical architecture ownership, measured automation improvement, or long-term infrastructure operations.
- Created a governance architecture for evaluating smart-contract-based compliance execution.
- Defined how programmable financial agreement behavior could remain subject to lifecycle control.
- Positioned programmable compliance under institutional authority, governance control, and audit oversight.
- Clarified authority, escalation, and intervention requirements before deployment consideration.
- Mapped accountability across on-chain execution, off-chain systems, and human governance.
- Smart Contract Governance Lifecycle defined lifecycle governance across contract creation, approval, deployment, execution, monitoring, upgrade, change control, retirement, and decommissioning.
- Programmable Compliance Operating Model positioned smart contracts under institutional authority, compliance control, audit visibility, and governance oversight.
- Execution Authority and Escalation Model defined authority delegation, separation of duties, activation controls, intervention rights, and escalation pathways across governance and execution layers.
- On-Chain and Off-Chain Responsibility Framework defined responsibility boundaries across programmable execution, institutional systems, human governance, audit evidence, and regulatory accountability expectations.
- The model translated smart contract execution mechanics into governance control requirements.
- The model clarified that programmable execution should remain subject to institutional intervention capability and human authority.
- Governance lifecycle completeness across creation, approval, deployment, execution, monitoring, upgrade, and retirement.
- Authority delegation clarity, separation-of-duties coverage, escalation readiness, and intervention control.
- Audit visibility across lifecycle events, execution behavior, approvals, changes, and interventions.
- Responsibility-boundary clarity across on-chain execution, off-chain systems, institutional data, and human governance.
- Permit programmable execution only under defined governance authority and lifecycle approval.
- Require institutional intervention capability before automated enforcement or deterministic execution advances.
- Require responsibility boundaries that preserve accountability across on-chain execution, off-chain systems, and human governance.
- Require audit visibility and alignment with existing institutional control frameworks before deployment feasibility is considered.
Brian completed the smart contract governance lifecycle, programmable compliance operating model, execution authority and escalation model, on-chain and off-chain responsibility framework, and decision logic that could support stakeholder review and deployment-feasibility evaluation. Production implementation, smart contract audit authority, regulatory approval, technical architecture ownership, deployed smart-contract systems, institutional adoption, measured automation outcomes, and long-term infrastructure operations remained outside the scope of the case.