CASE STUDY
Enterprise Governance & Policy Architecture for AI Systems
Institutionalizing the authority, risk taxonomy, capital discipline, vendor governance, and oversight model required before AI can scale in a regulated enterprise.
CASE STUDY
Institutionalizing the authority, risk taxonomy, capital discipline, vendor governance, and oversight model required before AI can scale in a regulated enterprise.
AI Governance
Enterprise Decision Systems
Capital Discipline
INSTITUTIONAL GOVERNANCE
Conceptual Transformation Scenario
AI & Product Strategy Lead
Brian designed an enterprise AI governance operating model that translated fragmented AI activity into a structured control system for responsible adoption. The work established how AI initiatives could be classified, authorized, funded, monitored, escalated, and governed before further scale.
A Regulated Financial-services Institution needed a way to preserve business ownership while creating consistent enterprise controls for AI risk, funding discipline, vendor exposure, and executive oversight. Brian created four institutional artifacts — an AI charter, portfolio risk taxonomy, capital allocation governance model, and vendor governance / build-vs-buy framework — that made governance authority, decision thresholds, and oversight requirements more explicit and decision-ready.
AI activity was increasing across the institution, but governance was fragmented across business units, jurisdictions, functions, funding decisions, and sourcing paths. Governance maturity had not kept pace with adoption pressure.
The problem was not AI interest. The problem was institutional control.
The challenge was leadership lacked a consistent system for determining which AI initiatives could proceed, what level of oversight they required, how funding should be conditioned, which vendor exposures needed escalation, and when executive or board review was necessary.
The opportunity was to define an enterprise AI governance operating model that could turn fragmented experimentation into controlled adoption by connecting authority, risk classification, capital discipline, vendor governance, escalation, and oversight before further AI scale.
How could a global financial institution move from fragmented AI experimentation to controlled enterprise adoption by defining risk-tiered authority, capital gating, vendor governance, and executive / board oversight before further AI scale?
In a regulated financial institution, fragmented AI adoption can create inconsistent validation standards, limited portfolio visibility, unclear decision authority, uncontrolled vendor exposure, and capital allocation disconnected from risk readiness.
I led the design of the enterprise AI governance operating model, translating fragmented AI activity into a structured control system for responsible adoption. My role focused on clarifying how AI initiatives would be classified, authorized, funded, monitored, sourced, escalated, and reviewed across a regulated enterprise.
This was an independent enterprise AI strategy and governance case developed as a conceptual transformation scenario for a regulated financial-services environment. I structured the governance problem around institutional authority, portfolio risk classification, funding eligibility, vendor exposure, and executive oversight, then translated that logic into decision-ready artifacts.
The work established a governance architecture that could help leadership determine what could move forward, what required remediation, what needed executive review, and what should not receive capital until governance conditions were met.
My responsibilities included:
This case demonstrates independent strategy, operating-model design, governance architecture, decision logic, and institutional artifacts. It does not claim client-enterprise deployment, production implementation, legal interpretation, audit execution, board authority, institutional adoption, measured risk reduction, or realized financial outcomes.
Brian designed the end-to-end governance architecture for classifying AI initiatives, defining authority and escalation logic, conditioning capital release, evaluating vendor sourcing paths, and translating institutional AI governance into artifacts that could support implementation planning and executive decision-making.
The solution was an enterprise AI governance operating model that connected institutional authority, risk classification, capital discipline, vendor control, escalation, and executive oversight into one decision system.
Instead of treating governance as a policy document or review checklist, the model defined how AI initiatives should be classified, conditioned, funded, sourced, monitored, and escalated before broader adoption.
The solution connected four governance questions:
Together, these components created a governance architecture for moving from decentralized experimentation to controlled enterprise AI adoption while preserving business ownership within consistent institutional controls.
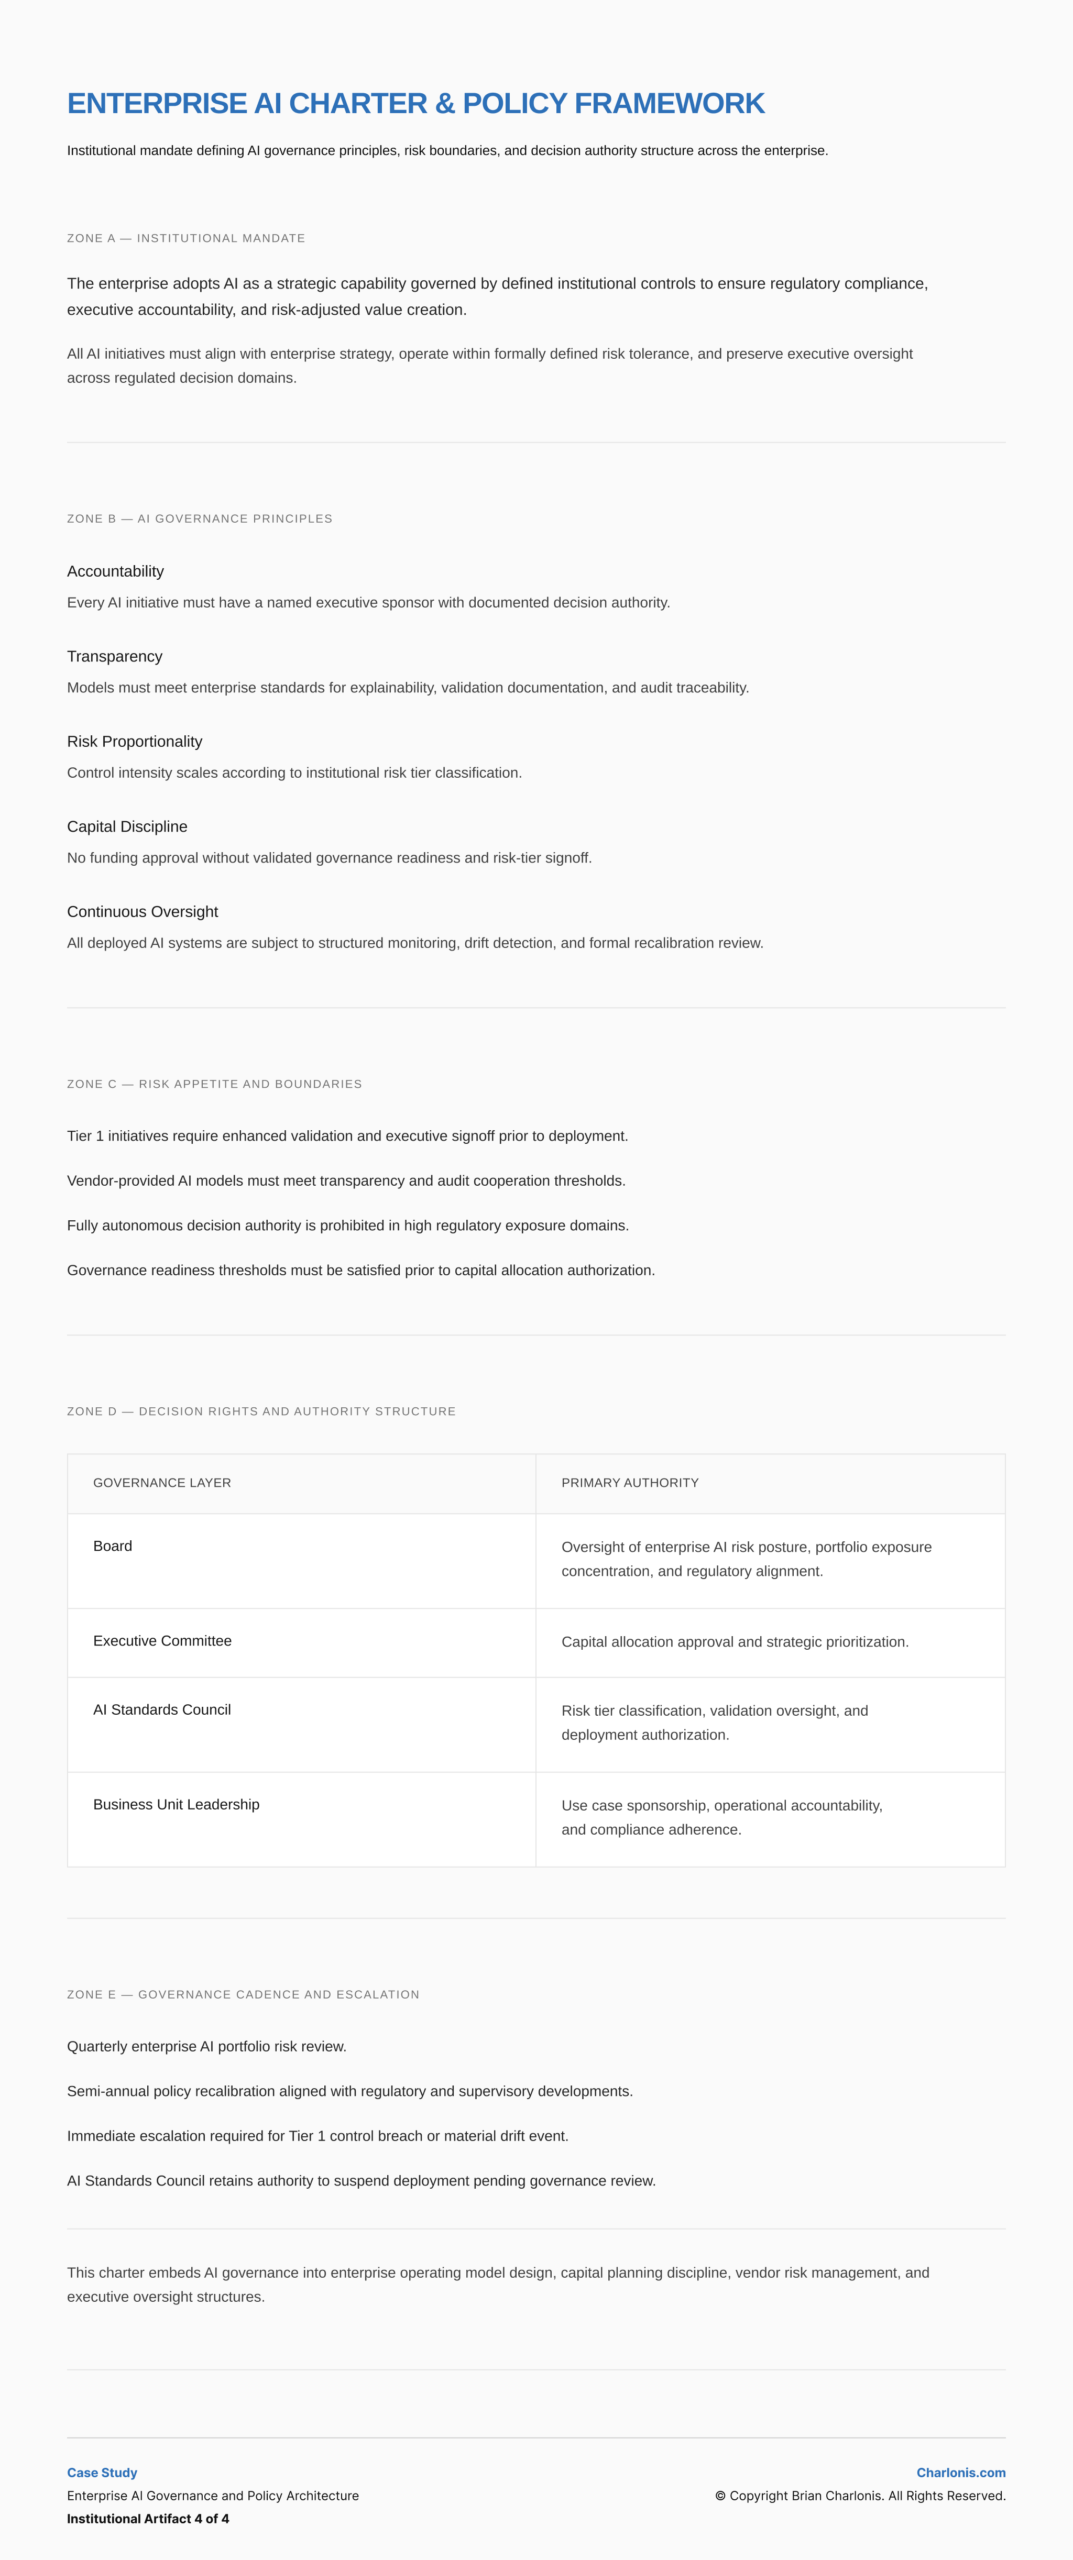
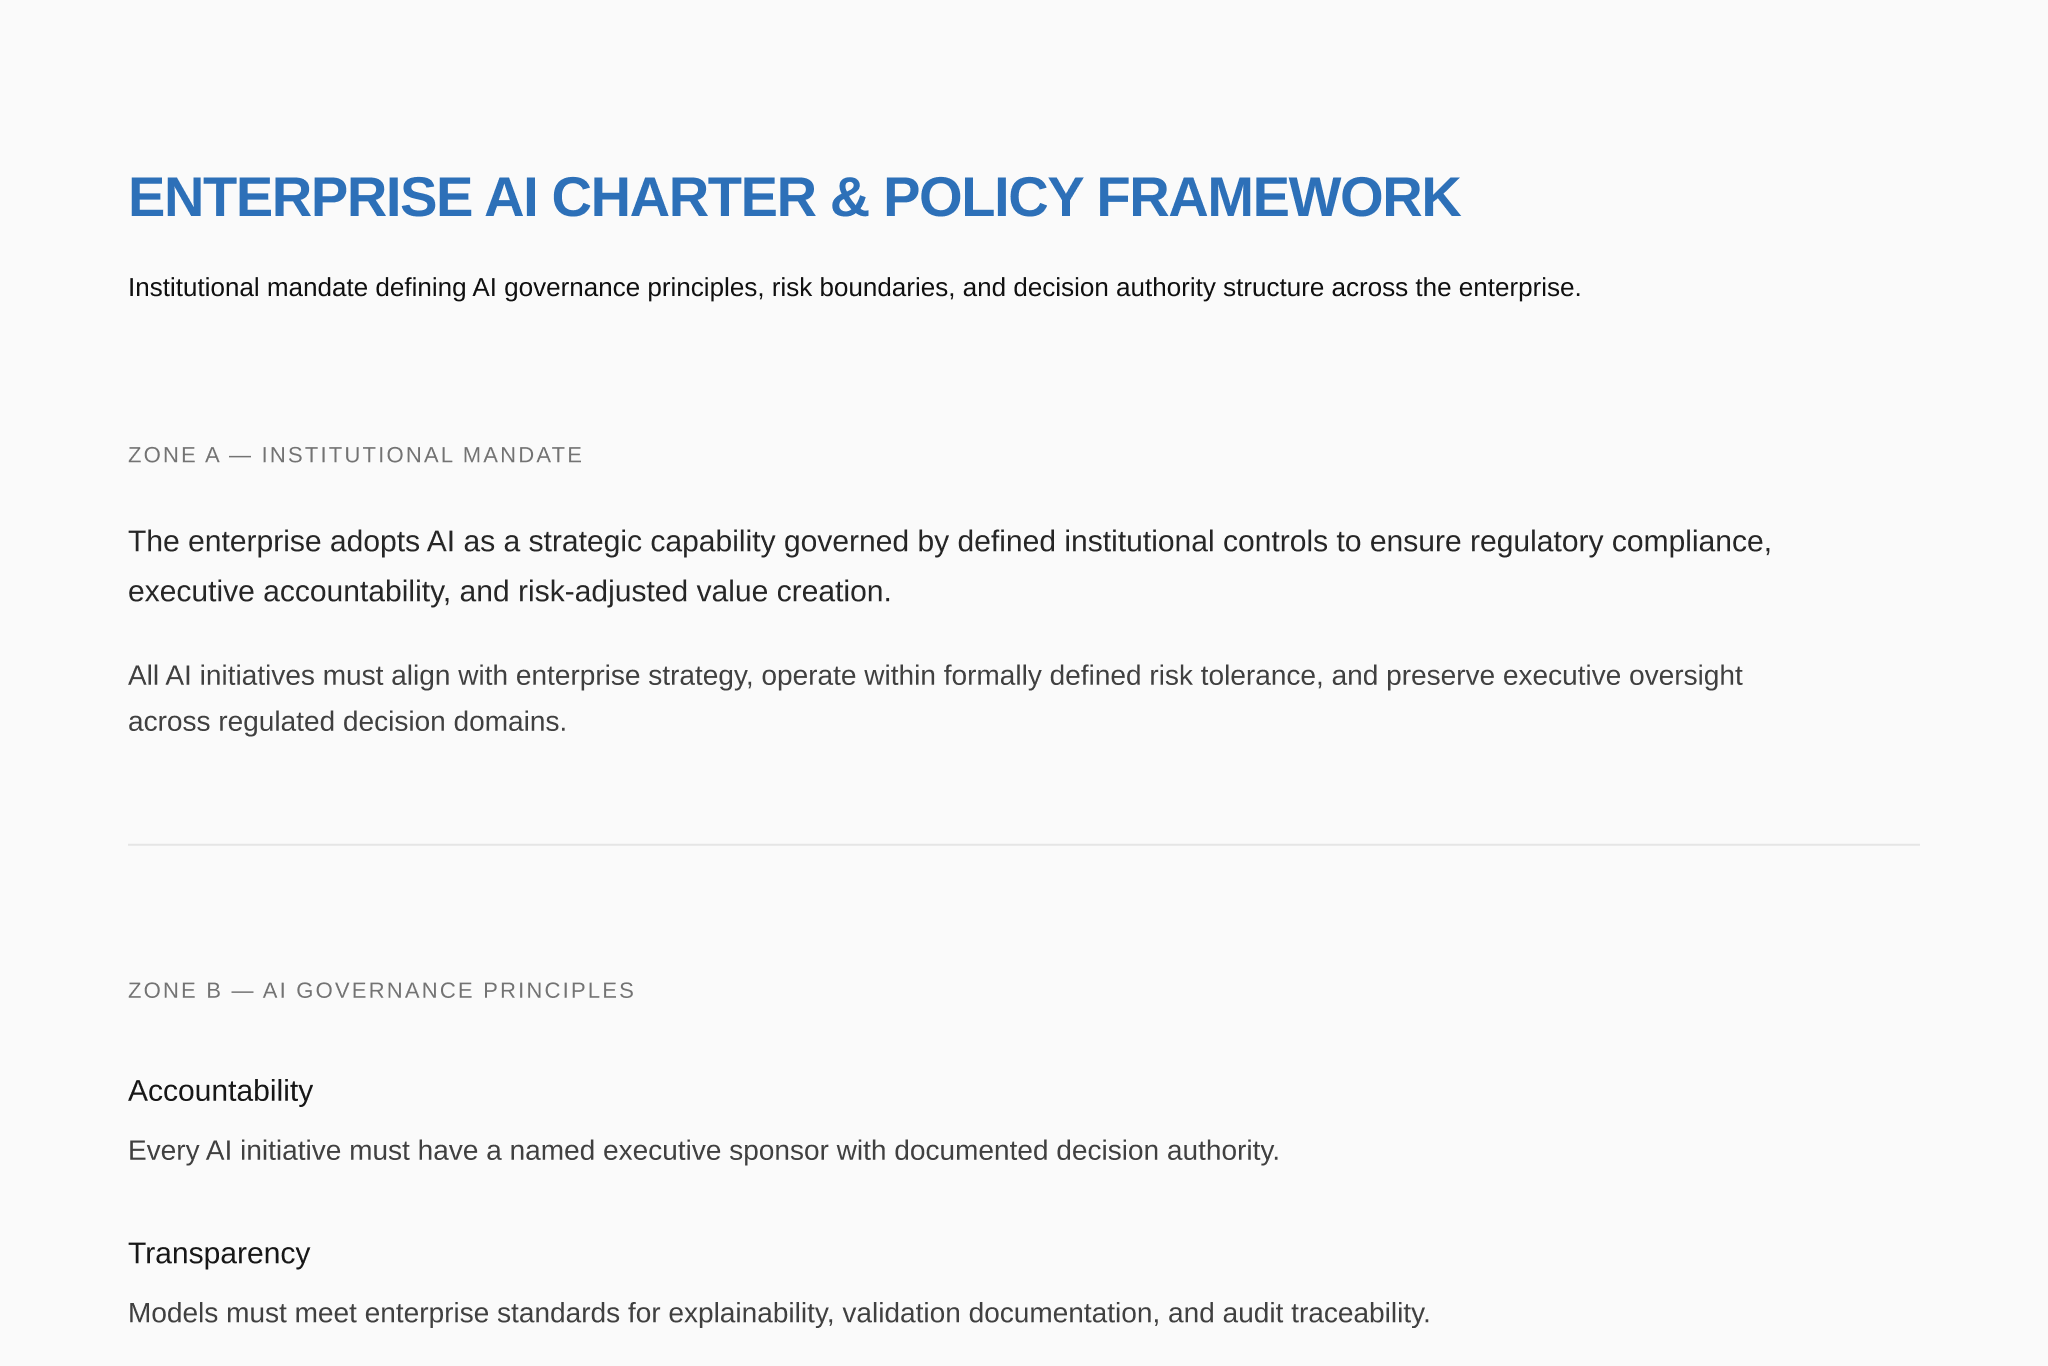
The charter established the institutional mandate, governance principles, risk boundaries, decision rights, and oversight cadence for enterprise AI. It clarified that AI should be treated as a strategic capability governed through formal authority, with clear rules for approval, challenge, escalation, conditional approval, suspension, and oversight.
Key Elements
Artifact type: Institutional governance framework.
The artifact translated the governance mandate into decision rights, authority layers, risk boundaries, and escalation expectations that could guide enterprise AI oversight.
The artifact translated the governance mandate into decision rights, authority layers, risk boundaries, and escalation expectations that could guide enterprise AI oversight.
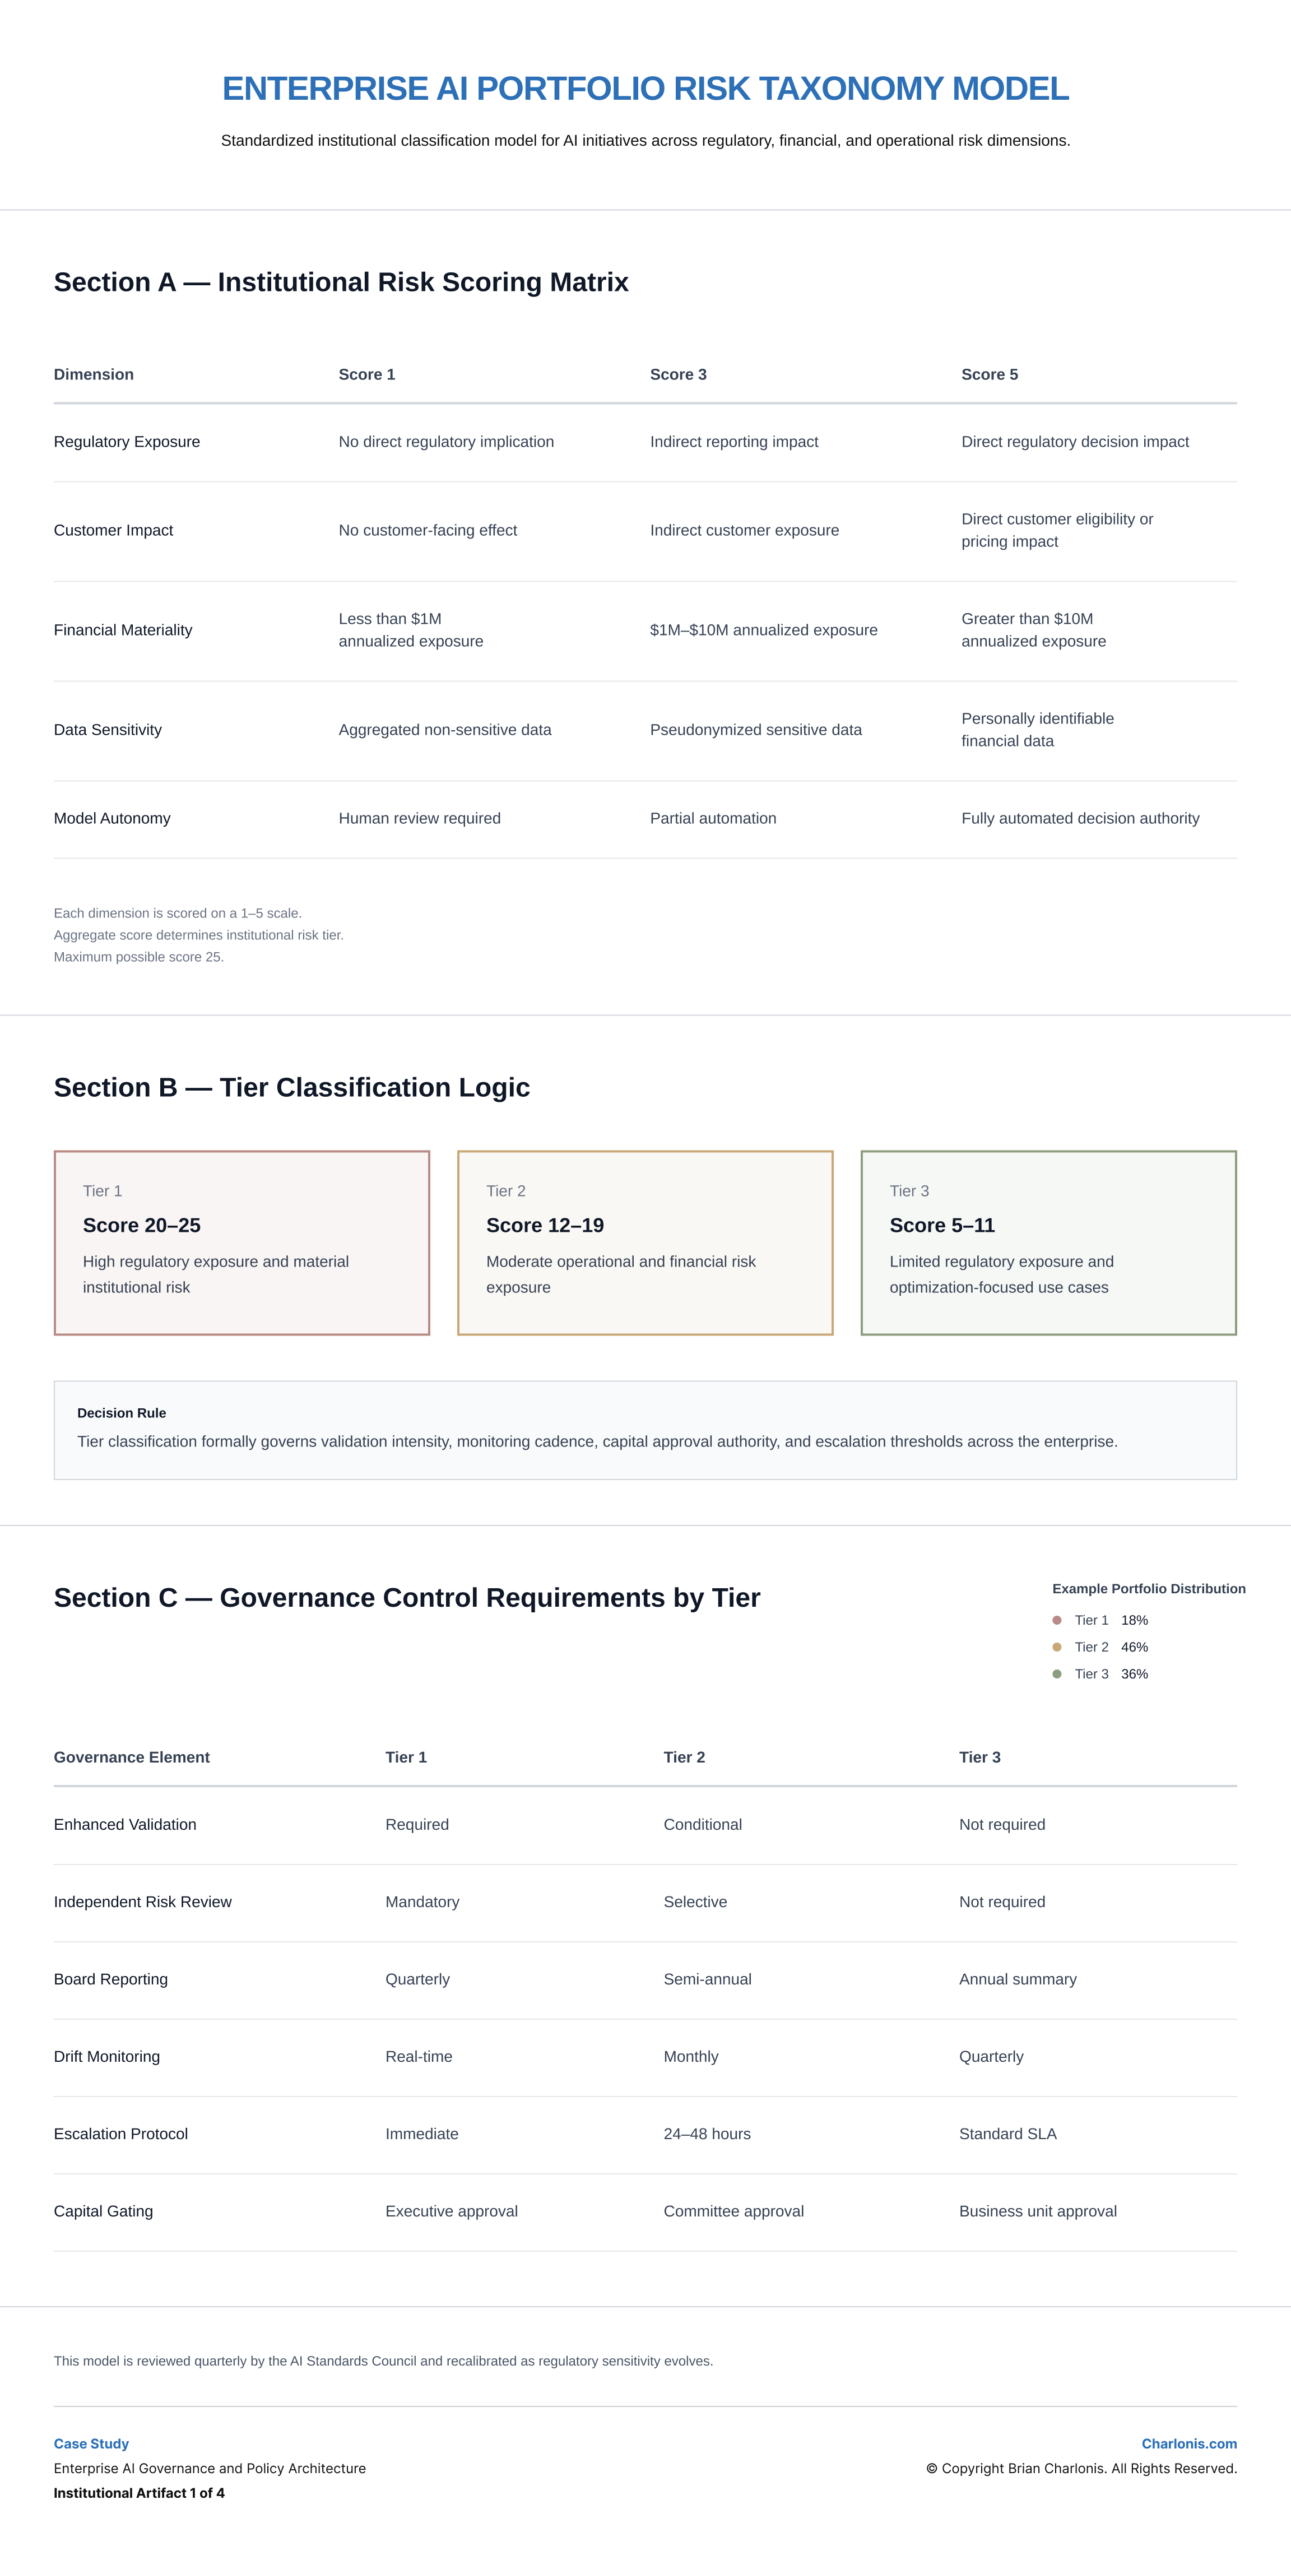
The risk taxonomy created a standardized classification model for AI initiatives across regulatory, financial, customer, data, and autonomy dimensions. It established a common language for distinguishing lower-risk optimization use cases from higher-impact initiatives requiring enhanced validation, monitoring, capital controls, or executive visibility.
Key Elements
Artifact type: Risk classification and control model.
The artifact showed how initiatives could be scored, classified, and routed into proportionate governance requirements based on material exposure.
This component would support AI Standards Council review, business-unit planning, executive reporting, and capital approval decisions by making risk classification consistent across use cases and jurisdictions. It clarified which initiatives required standard review, enhanced validation, executive escalation, board visibility, remediation, funding restriction, or delayed approval.
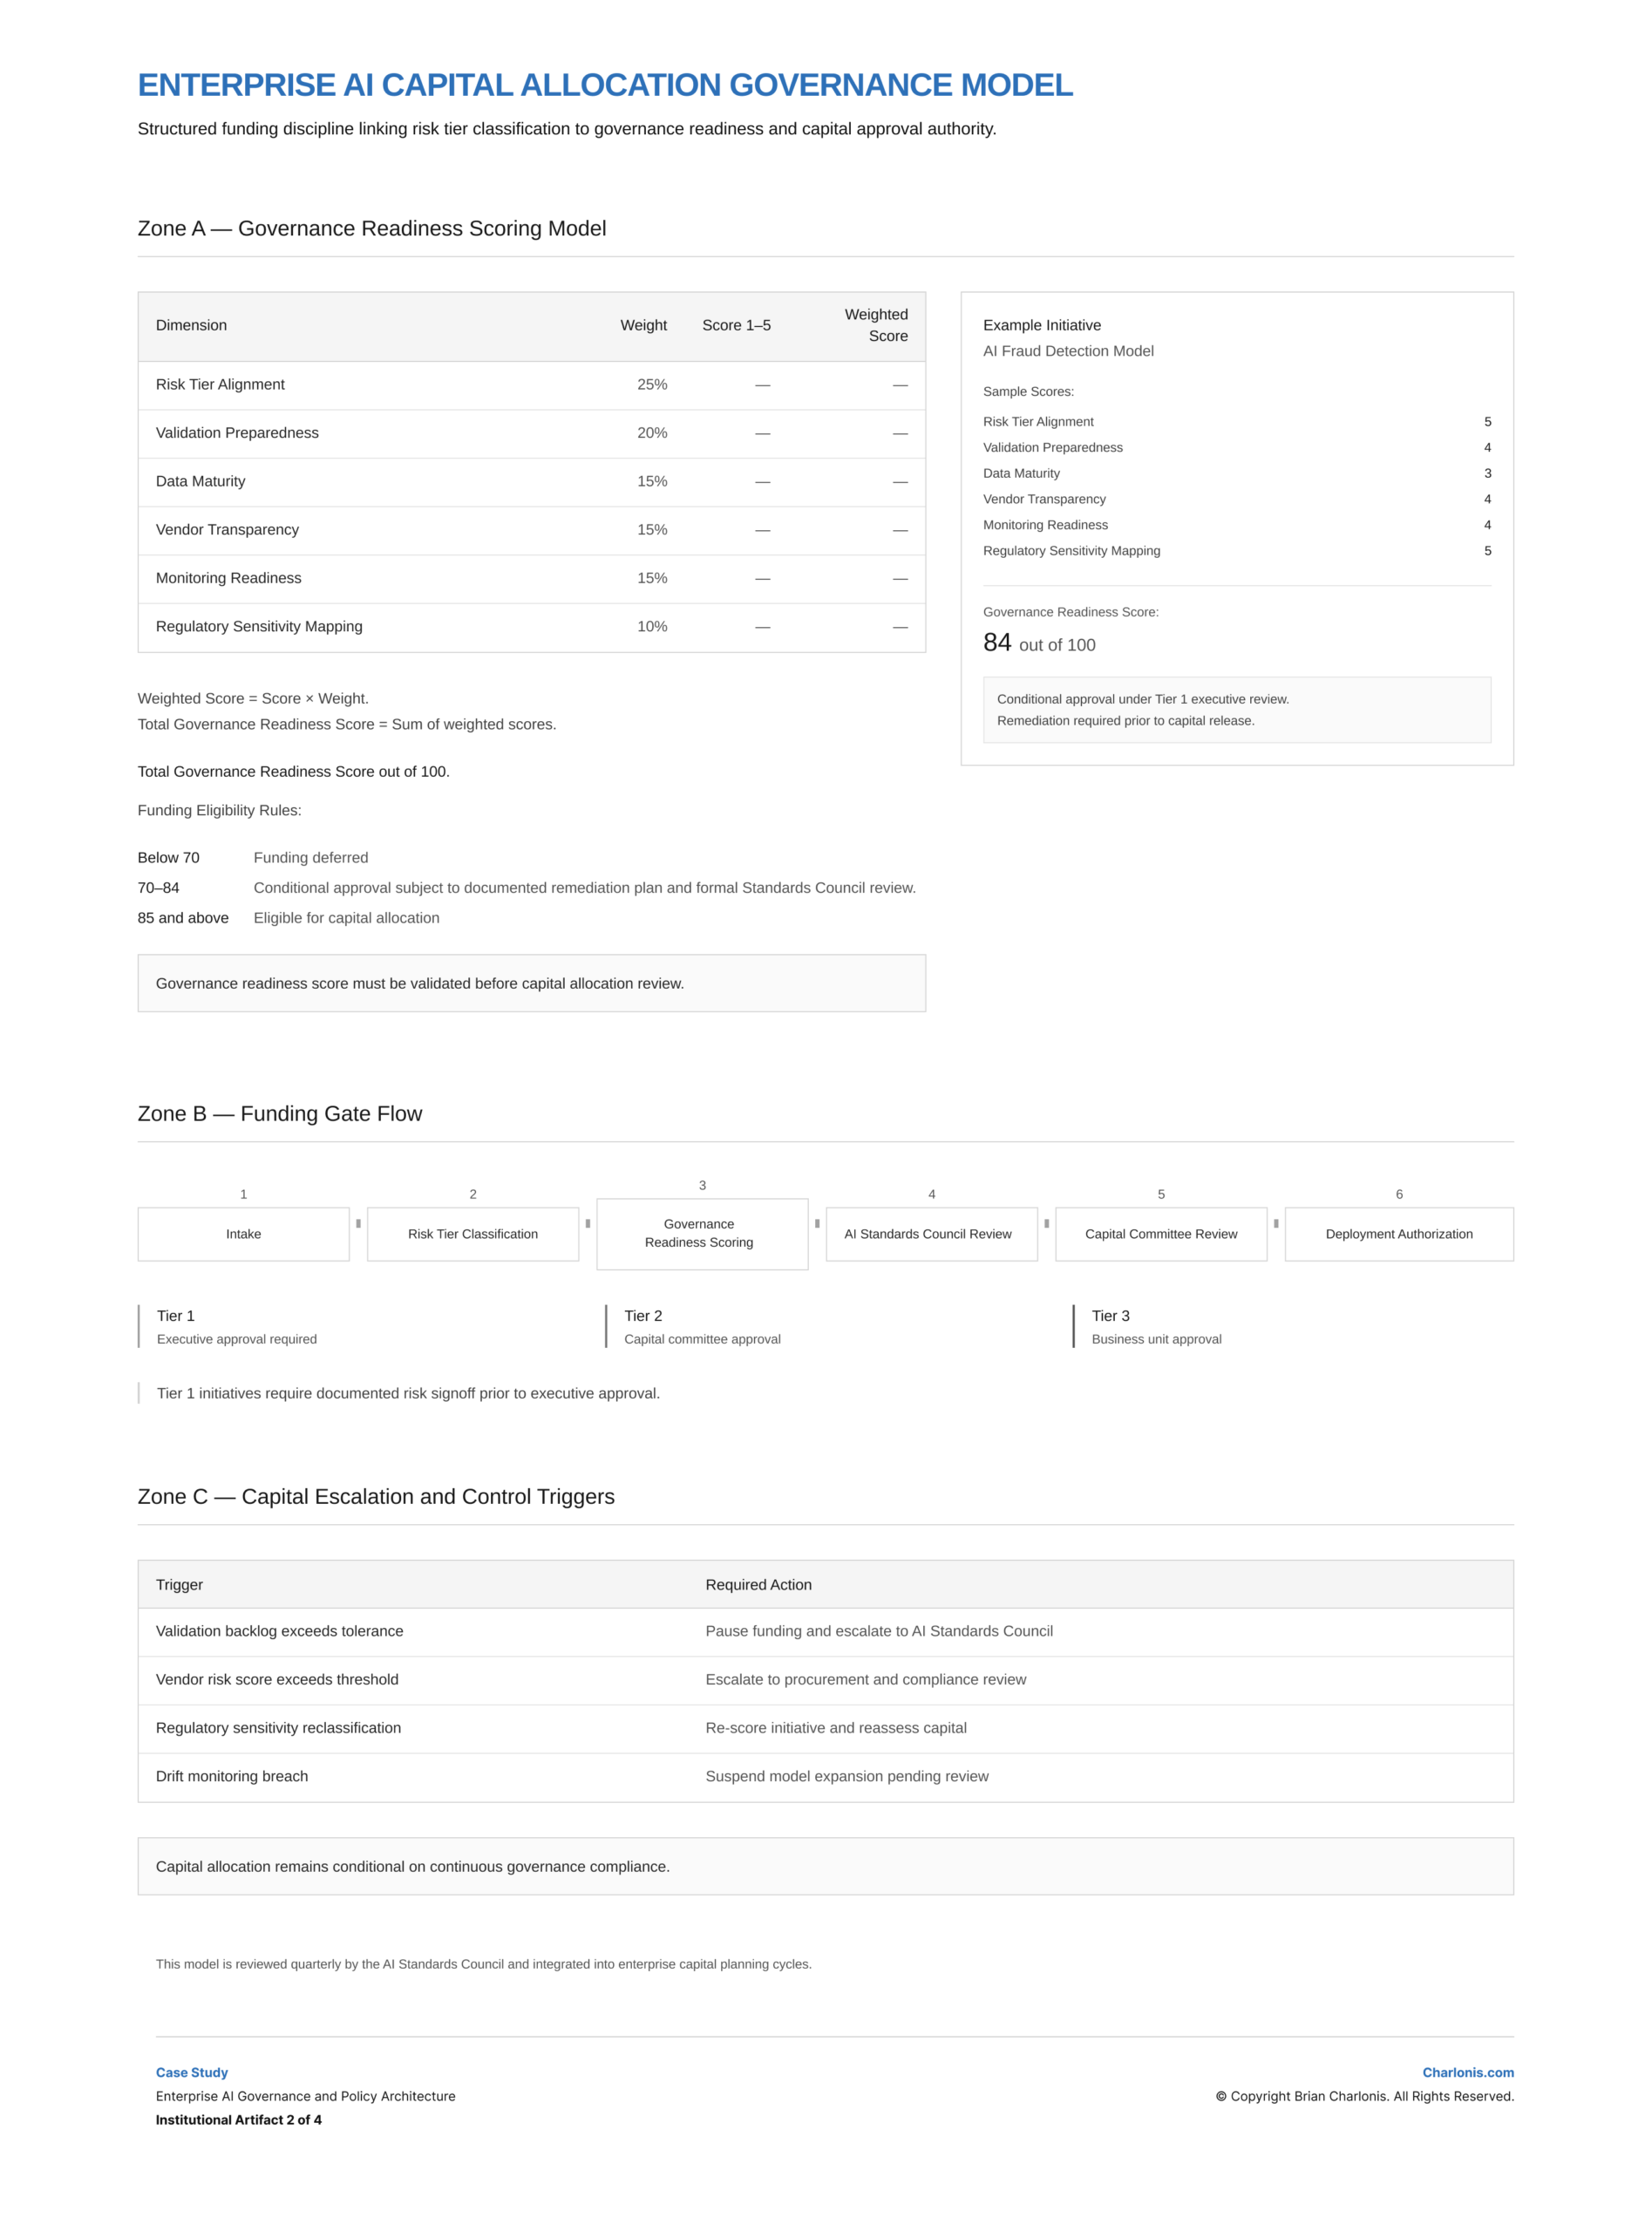
The capital allocation model connected funding eligibility to risk tier, governance readiness, validation preparedness, control maturity, vendor transparency, monitoring readiness, and regulatory sensitivity. It treated capital release as a governance control, ensuring that promising AI initiatives could not move forward on business-case appeal alone.
Key Elements
Artifact type: Funding gate and governance-readiness model.
The artifact showed how governance readiness scoring, funding rules, executive review, and control triggers could be connected before capital allocation.
This component would support capital committee review, AI Standards Council oversight, and executive funding decisions by clarifying when initiatives were eligible for capital, conditionally approved, remediated, escalated, paused, or restricted. It made funding eligibility dependent on governance readiness rather than urgency, enthusiasm, or isolated technical promise.
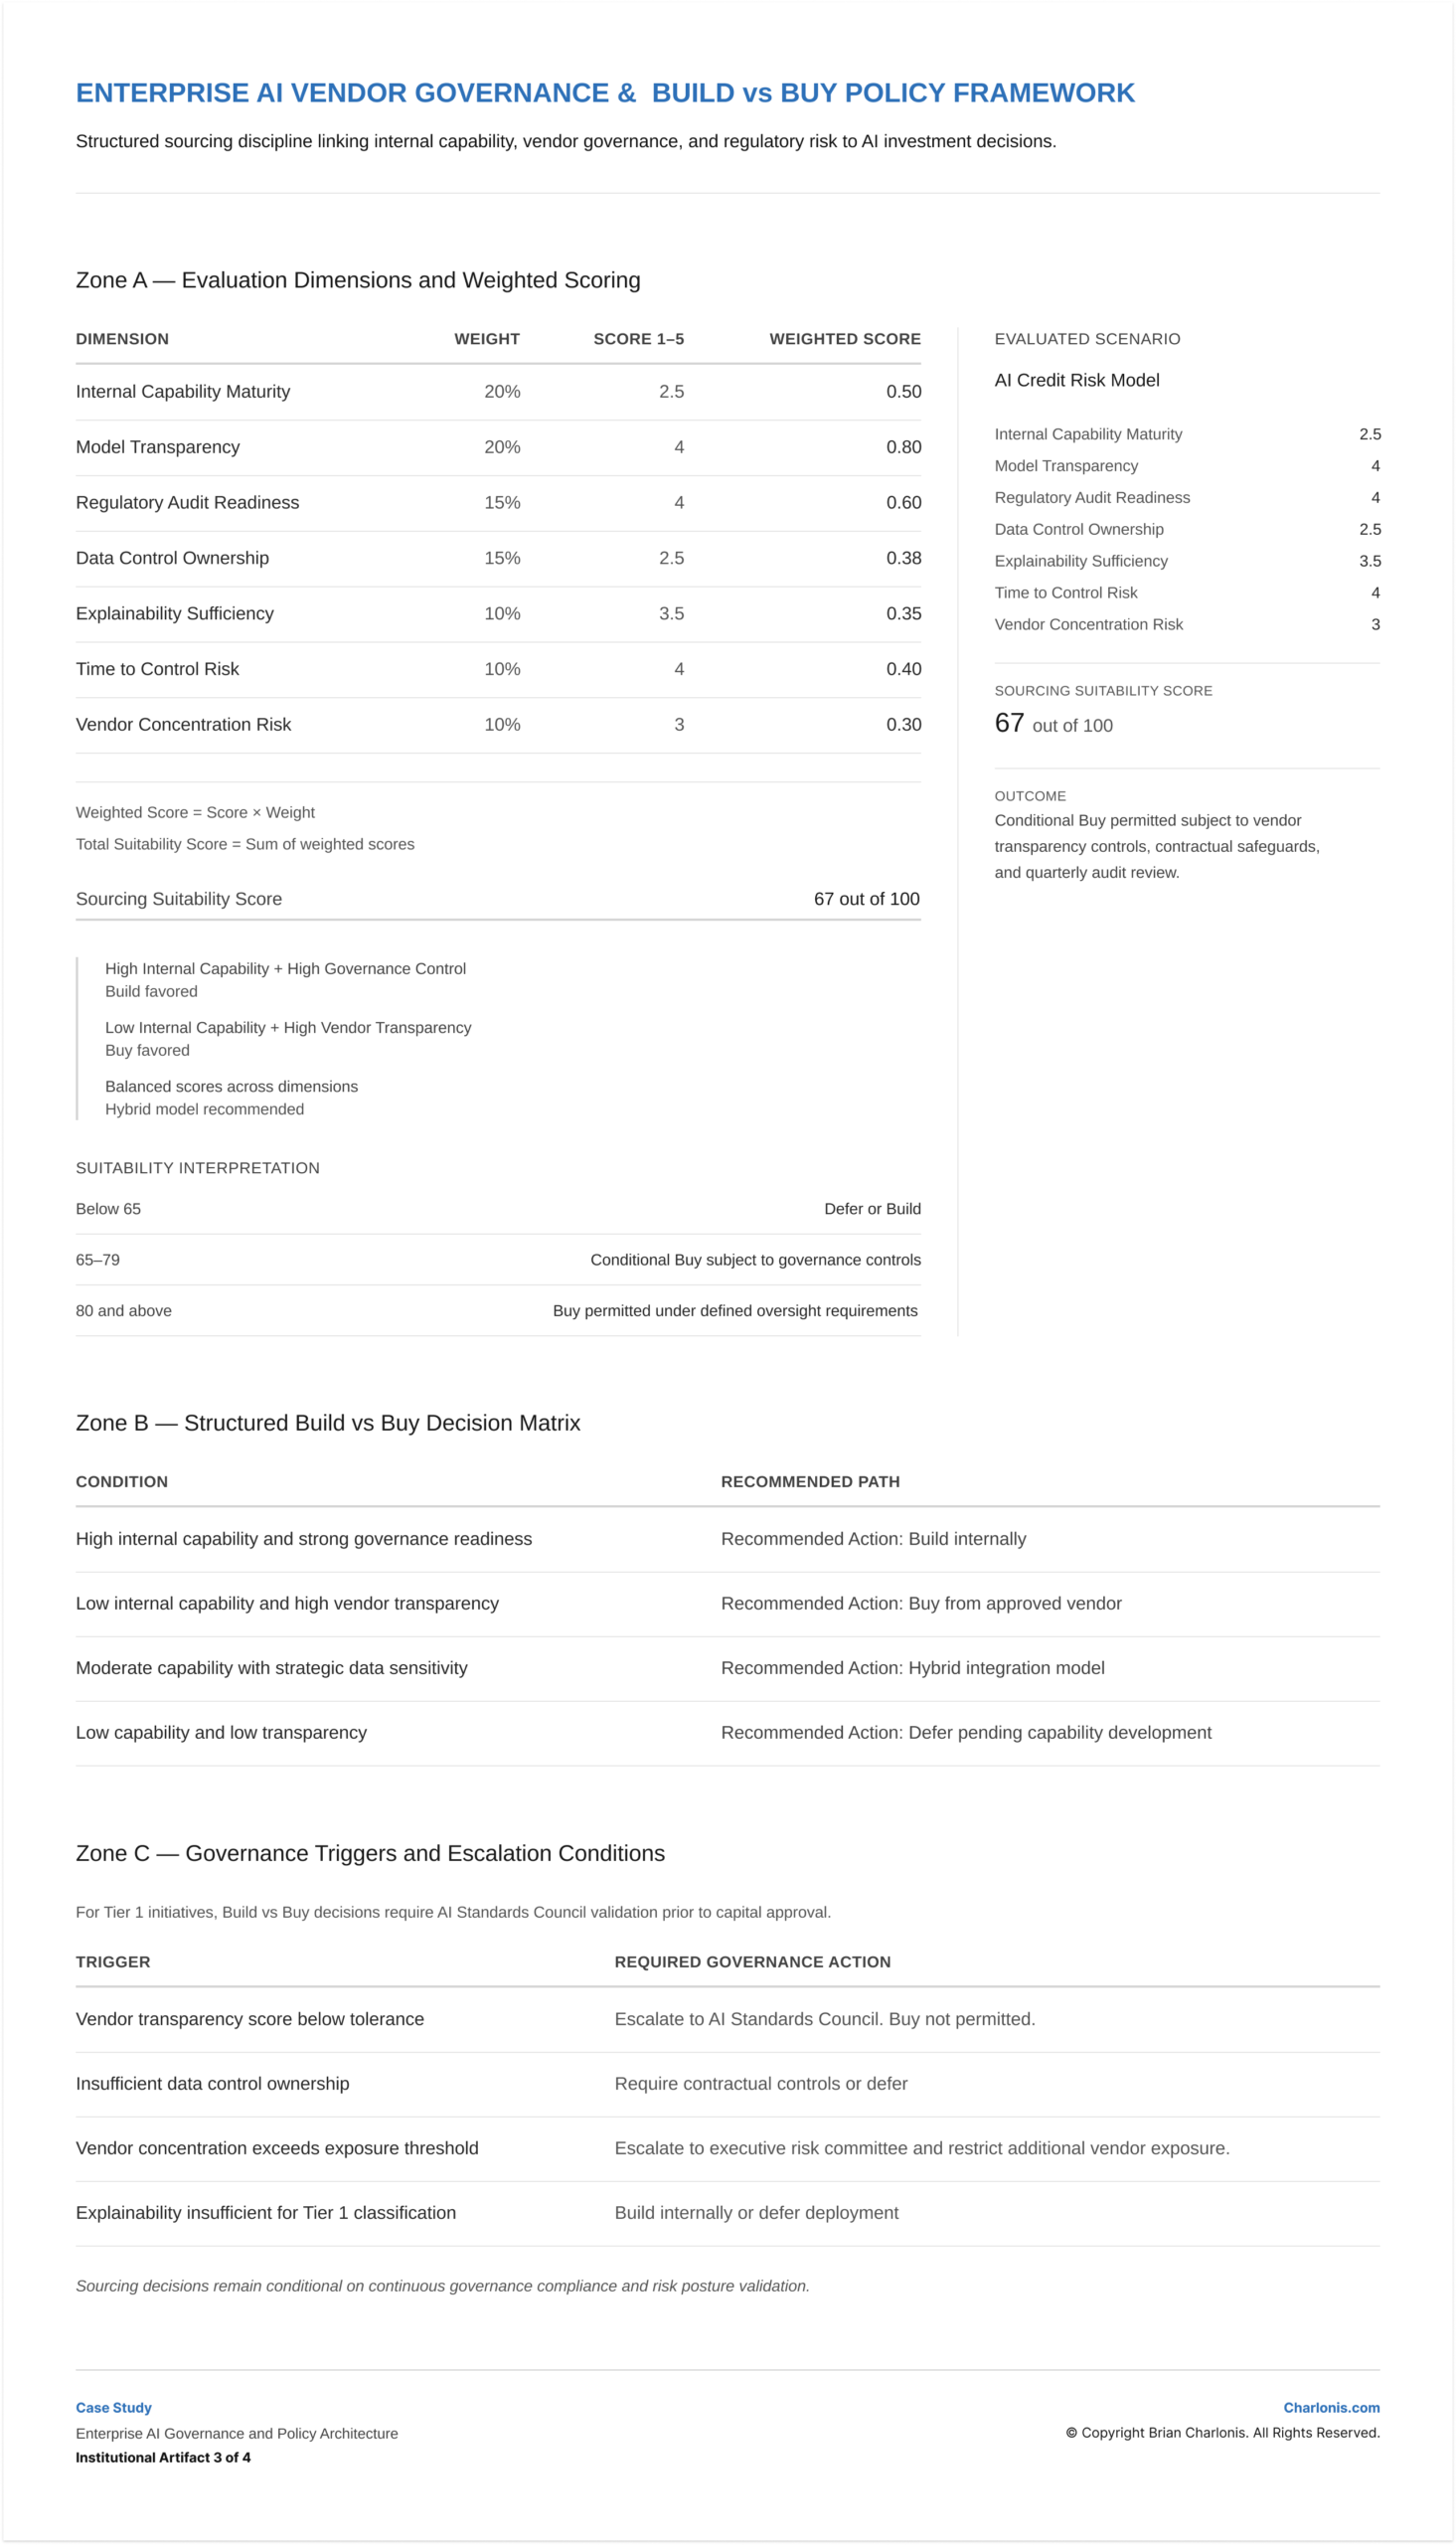
The vendor governance framework connected AI sourcing decisions to institutional capability, vendor transparency, audit readiness, data control, explainability, time-to-control risk, and concentration exposure. It positioned build-vs-buy decisions as enterprise governance decisions rather than procurement or delivery-speed choices alone.
Key Elements
Artifact type: Vendor governance and sourcing decision framework.
The artifact showed how sourcing decisions could be scored, interpreted, and escalated based on control maturity, vendor exposure, and institutional risk.
This component would support business, procurement, risk, compliance, and technology leaders in deciding whether to build internally, buy from an approved vendor, use a hybrid integration model, defer pending capability development, or escalate when transparency, data control, or concentration risk exceeded tolerance. It clarified how fragmented vendor adoption could be prevented from becoming unmanaged enterprise exposure.
This case produced an enterprise AI governance operating model, four institutional artifacts, and decision-ready logic for authority, classification, capital gating, vendor governance, escalation, and oversight. It was developed as an independent conceptual enterprise strategy case and does not claim production deployment, institutional adoption, measured risk reduction, or realized capital-allocation outcomes.
Brian completed the governance architecture, decision logic, and institutional artifacts that could support implementation planning, executive review, and phased governance adoption. Legal interpretation, technical implementation, model validation, audit execution, board authority, production deployment, institutional adoption, and realized financial outcomes remained outside the scope of the case.
The central challenge was not whether the institution could pursue more AI initiatives.
It was whether the organization could scale AI adoption through authority, risk classification, capital discipline, vendor control, and executive oversight without allowing fragmented experimentation to become unmanaged institutional exposure.
AI could improve governance operations by helping teams identify initiatives, classify risk inputs, detect readiness gaps, surface vendor exposure, retrieve policy requirements, and summarize portfolio-level oversight signals. Human authority and validation would remain necessary for approvals, capital release, risk acceptance, policy interpretation, and consequential governance decisions; conventional governance systems may remain sufficient where workflows are stable, evidence is complete, and escalation logic is already clear.
CASE STUDY
DATA & RESPONSIBLE AI GOVERNANCE
Defined a Data and Responsible AI Governance operating model connecting risk-tiered intake, accountable business ownership, cross-functional controls, lifecycle oversight, reassessment, and executive visibility without routing every AI decision through one centralized approval bottleneck.
Data & Responsible AI Governance
Lifecycle Governance
Decision Rights
CASE STUDY
FEDERATED AI ADOPTION
Defined a federated AI adoption model for a decentralized software portfolio, connecting business-unit readiness, local ownership, workflow-change evidence, value signals, and cross-unit learning to move AI adoption beyond tool access and isolated pilots.
AI Adoption
Enterprise AI Adoption
Federated Operating Model

CASE STUDY
OPERATIONAL AI GOVERNANCE
Defined a human-in-the-loop governance model for regulated AI-assisted decisions, establishing confidence thresholds, escalation controls, override tolerance, monitoring signals, synthetic scenario comparison, and recalibration logic for when automation should defer to human judgment.
Operational AI Governance
Human-in-the-Loop Decision Systems
Monitoring & Recalibration

CASE STUDY
STRATEGIC OPERATING MODEL
A governed AI-assisted intelligence system designed, implemented, and operated to turn fragmented signals, evidence, and professional knowledge into structured decisions, accountable execution, reviewed artifacts, and controlled learning.
Decision Systems
AI Strategy
Enterprise Operating Models
I help regulated enterprises define the governance authority, capital discipline, vendor oversight & executive accountability required to move AI from experimentation to controlled adoption.