
Designing Programmable Compliance Infrastructure Using Smart Contracts
Structuring how smart-contract-based financial agreement execution could operate inside institutional governance, lifecycle controls, escalation pathways, audit visibility, and responsibility boundaries.
Programmable Compliance
Smart Contracts
Governed Financial Infrastructure
SMART CONTRACTS
Conceptual Transformation Scenario
Web3 Product & Strategy Lead
Brian designed a governance architecture for evaluating smart-contract-based financial agreement execution in regulated institutional environments. The work focused on lifecycle governance, institutional authority, programmable compliance controls, escalation pathways, audit visibility, and responsibility boundaries across on-chain execution, off-chain systems, and human governance.
A Global Financial Institution examined whether smart contracts could support automated financial agreement behavior without weakening institutional authority, accountability, auditability, or control. Brian created four artifacts: a Smart Contract Governance Lifecycle, Programmable Compliance Operating Model, Execution Authority and Escalation Model, and On-Chain and Off-Chain Responsibility Framework, that clarified how programmable execution could be evaluated as governed financial infrastructure rather than autonomous code operating outside institutional oversight.
CHALLENGE
Financial institutions operate under strict regulatory, audit, and control requirements designed to preserve accountability across financial agreement execution.
Smart contracts introduced the ability to encode financial agreement behavior into programmable execution paths, including covenant enforcement, collateral monitoring, and compliance-related controls.
However, existing governance models were not designed for deterministic execution that could trigger actions based on predefined logic. This created a structural gap between institutional control frameworks and automated execution systems
The challenge was not whether smart contracts could automate rules. It was defining how programmable execution could operate inside institutional authority, regulatory accountability, audit requirements, and human intervention controls.
The opportunity was to design a governance architecture that helped leadership evaluate programmable compliance before deployment feasibility was considered.
Key Drivers
- Lack of lifecycle governance for smart contract deployment, monitoring, upgrade, and retirement.
- Absence of defined authority delegation and escalation pathways.
- Unclear responsibility boundaries between automated execution and human oversight.
- Regulatory and audit requirements for institutional accountability and control.
- Need to automate compliance-related execution without weakening governance integrity.
- Need to align programmable execution with existing institutional control frameworks.
Strategic Question
How could a global financial institution evaluate smart contracts as programmable compliance infrastructure while preserving lifecycle governance, institutional authority, escalation controls, audit visibility, and responsibility boundaries?
This required more than confirming that rules could be encoded into smart contracts. It required a governance model for determining who could approve, activate, pause, override, escalate, change, audit, or retire programmable financial agreement behavior.
MY ROLE
I served as Web3 Product and Strategy Lead, responsible for designing the governance architecture required to evaluate smart-contract-based compliance execution in a regulated institutional environment.
My role focused on translating smart contract execution mechanics into institutional control requirements, including lifecycle governance, authority delegation, escalation design, audit visibility, and responsibility boundaries across on-chain execution, off-chain systems, and human governance.
I structured the work so leadership could evaluate programmable compliance as governed financial infrastructure rather than autonomous automation outside institutional oversight.
My responsibilities included:
- Designing governance architecture for programmable compliance execution.
- Modeling lifecycle governance across contract creation, approval, deployment, execution, monitoring, upgrade, and retirement.
- Defining authority delegation, escalation pathways, and intervention controls.
- Mapping responsibility boundaries across on-chain execution, off-chain systems, and human governance.
- Translating audit and regulatory accountability requirements into governance controls.
- Aligning programmable execution concepts with enterprise architecture and institutional control frameworks.
This case demonstrates independent Web3 product strategy, governance architecture design, lifecycle control modeling, authority delegation logic, escalation design, audit-visibility definition, and responsibility-boundary mapping. It does not claim production smart-contract deployment, institutional adoption, regulatory approval authority, smart contract audit authority, technical architecture ownership, deployed smart-contract systems, measured automation outcomes, or long-term infrastructure operations.
Engagement at a Glance
Brian’s Scope
Brian designed the end-to-end programmable compliance governance model for evaluating smart contract lifecycle controls, institutional authority, escalation pathways, intervention rights, audit visibility, and accountability boundaries that could support stakeholder review and deployment-feasibility evaluation.
HOW I LED THE WORK
- Framed smart contracts as governed financial infrastructure, using institutional authority, regulatory accountability, audit visibility, and human intervention controls to move beyond a technology-first automation view.
- Started with lifecycle governance before execution mechanics, defining how programmable financial agreement behavior should move through creation, approval, deployment, execution, monitoring, upgrade, and retirement.
- Preserved institutional authority over automated behavior, positioning smart contracts inside governance, compliance, audit, and executive oversight rather than outside institutional control.
- Designed authority delegation and escalation logic, clarifying who could approve, activate, pause, intervene in, escalate, or change programmable execution behavior.
- Separated deterministic execution from institutional accountability, recognizing that automated behavior still required responsibility boundaries across code, data, systems, and human governance.
- Made audit visibility a design requirement, connecting lifecycle events, approvals, execution behavior, interventions, and responsibility boundaries to evidence expectations.
- Translated programmable compliance into decision-ready artifacts, giving leadership a structured way to evaluate feasibility through governance readiness rather than technical capability alone.
SOLUTION
The solution was a governance architecture for smart-contract-based programmable compliance, structured around lifecycle control, institutional authority, escalation and intervention rights, audit visibility, and responsibility boundaries across on-chain execution, off-chain systems, and human governance.
The solution connected four programmable compliance governance questions:
- How should programmable execution be governed across its lifecycle?
- How should programmable compliance operate inside institutional authority and control frameworks?
- Who has authority to approve, pause, escalate, intervene in, or change contract behavior?
- How should responsibility be divided across on-chain execution, off-chain systems, and human governance?
Together, these components created a governed operating model for evaluating smart-contract-based compliance execution before deployment feasibility or production implementation could be considered.
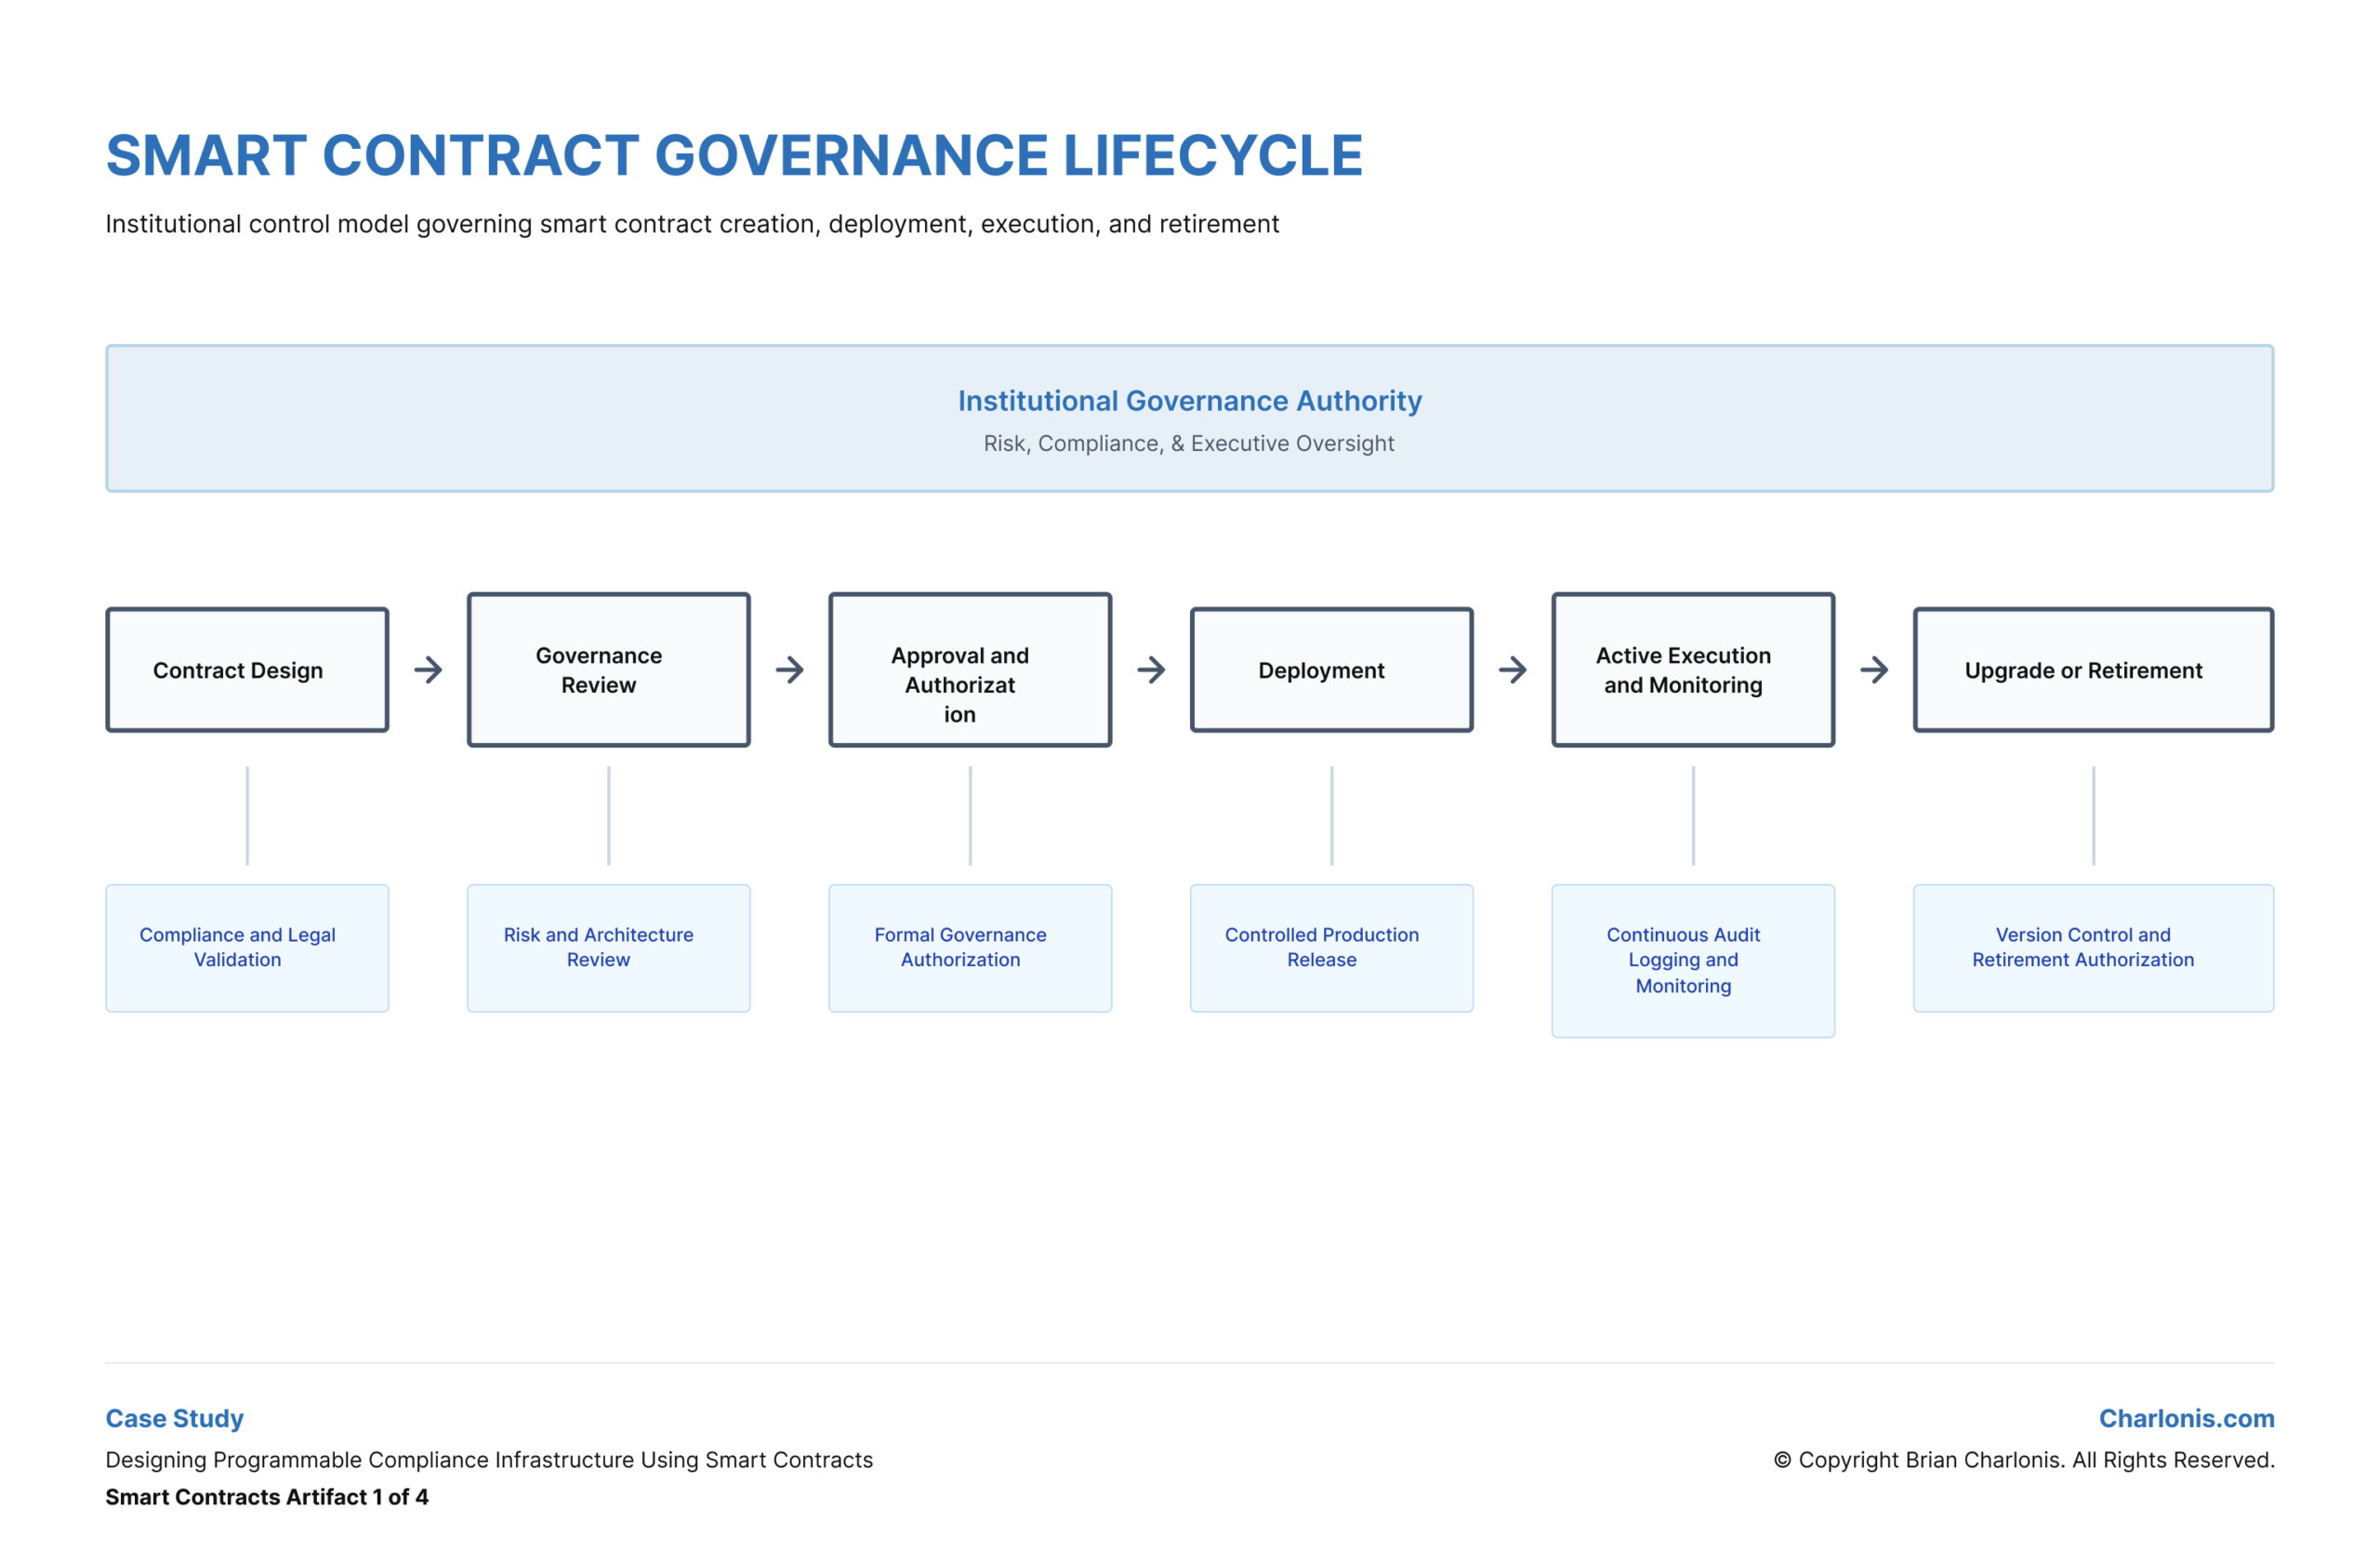
Smart Contract Governance Lifecycle
The governance lifecycle defined how programmable financial agreement behavior should move through creation, approval, deployment, execution, monitoring, upgrade, change control, retirement, and decommissioning while remaining subject to institutional governance. It clarified which checkpoints were required before smart-contract-based execution could move toward deployment consideration.
Key Elements
- Contract creation governance.
- Pre-deployment approval controls.
- Deployment authorization requirements.
- Execution monitoring expectations.
- Upgrade, change-control, retirement, and decommissioning pathways.
Artifact type: Governance lifecycle / contract-control model.
The artifact defined how programmable financial agreement behavior could move from creation through retirement while remaining subject to institutional authority, review, monitoring, and change control.
How It Shaped Decisions
This component would support governance, compliance, audit, and executive leadership stakeholders in determining which lifecycle stages required approval, how deployment readiness should be evaluated, where monitoring responsibilities should sit, and what governance conditions were required before upgrade or retirement.
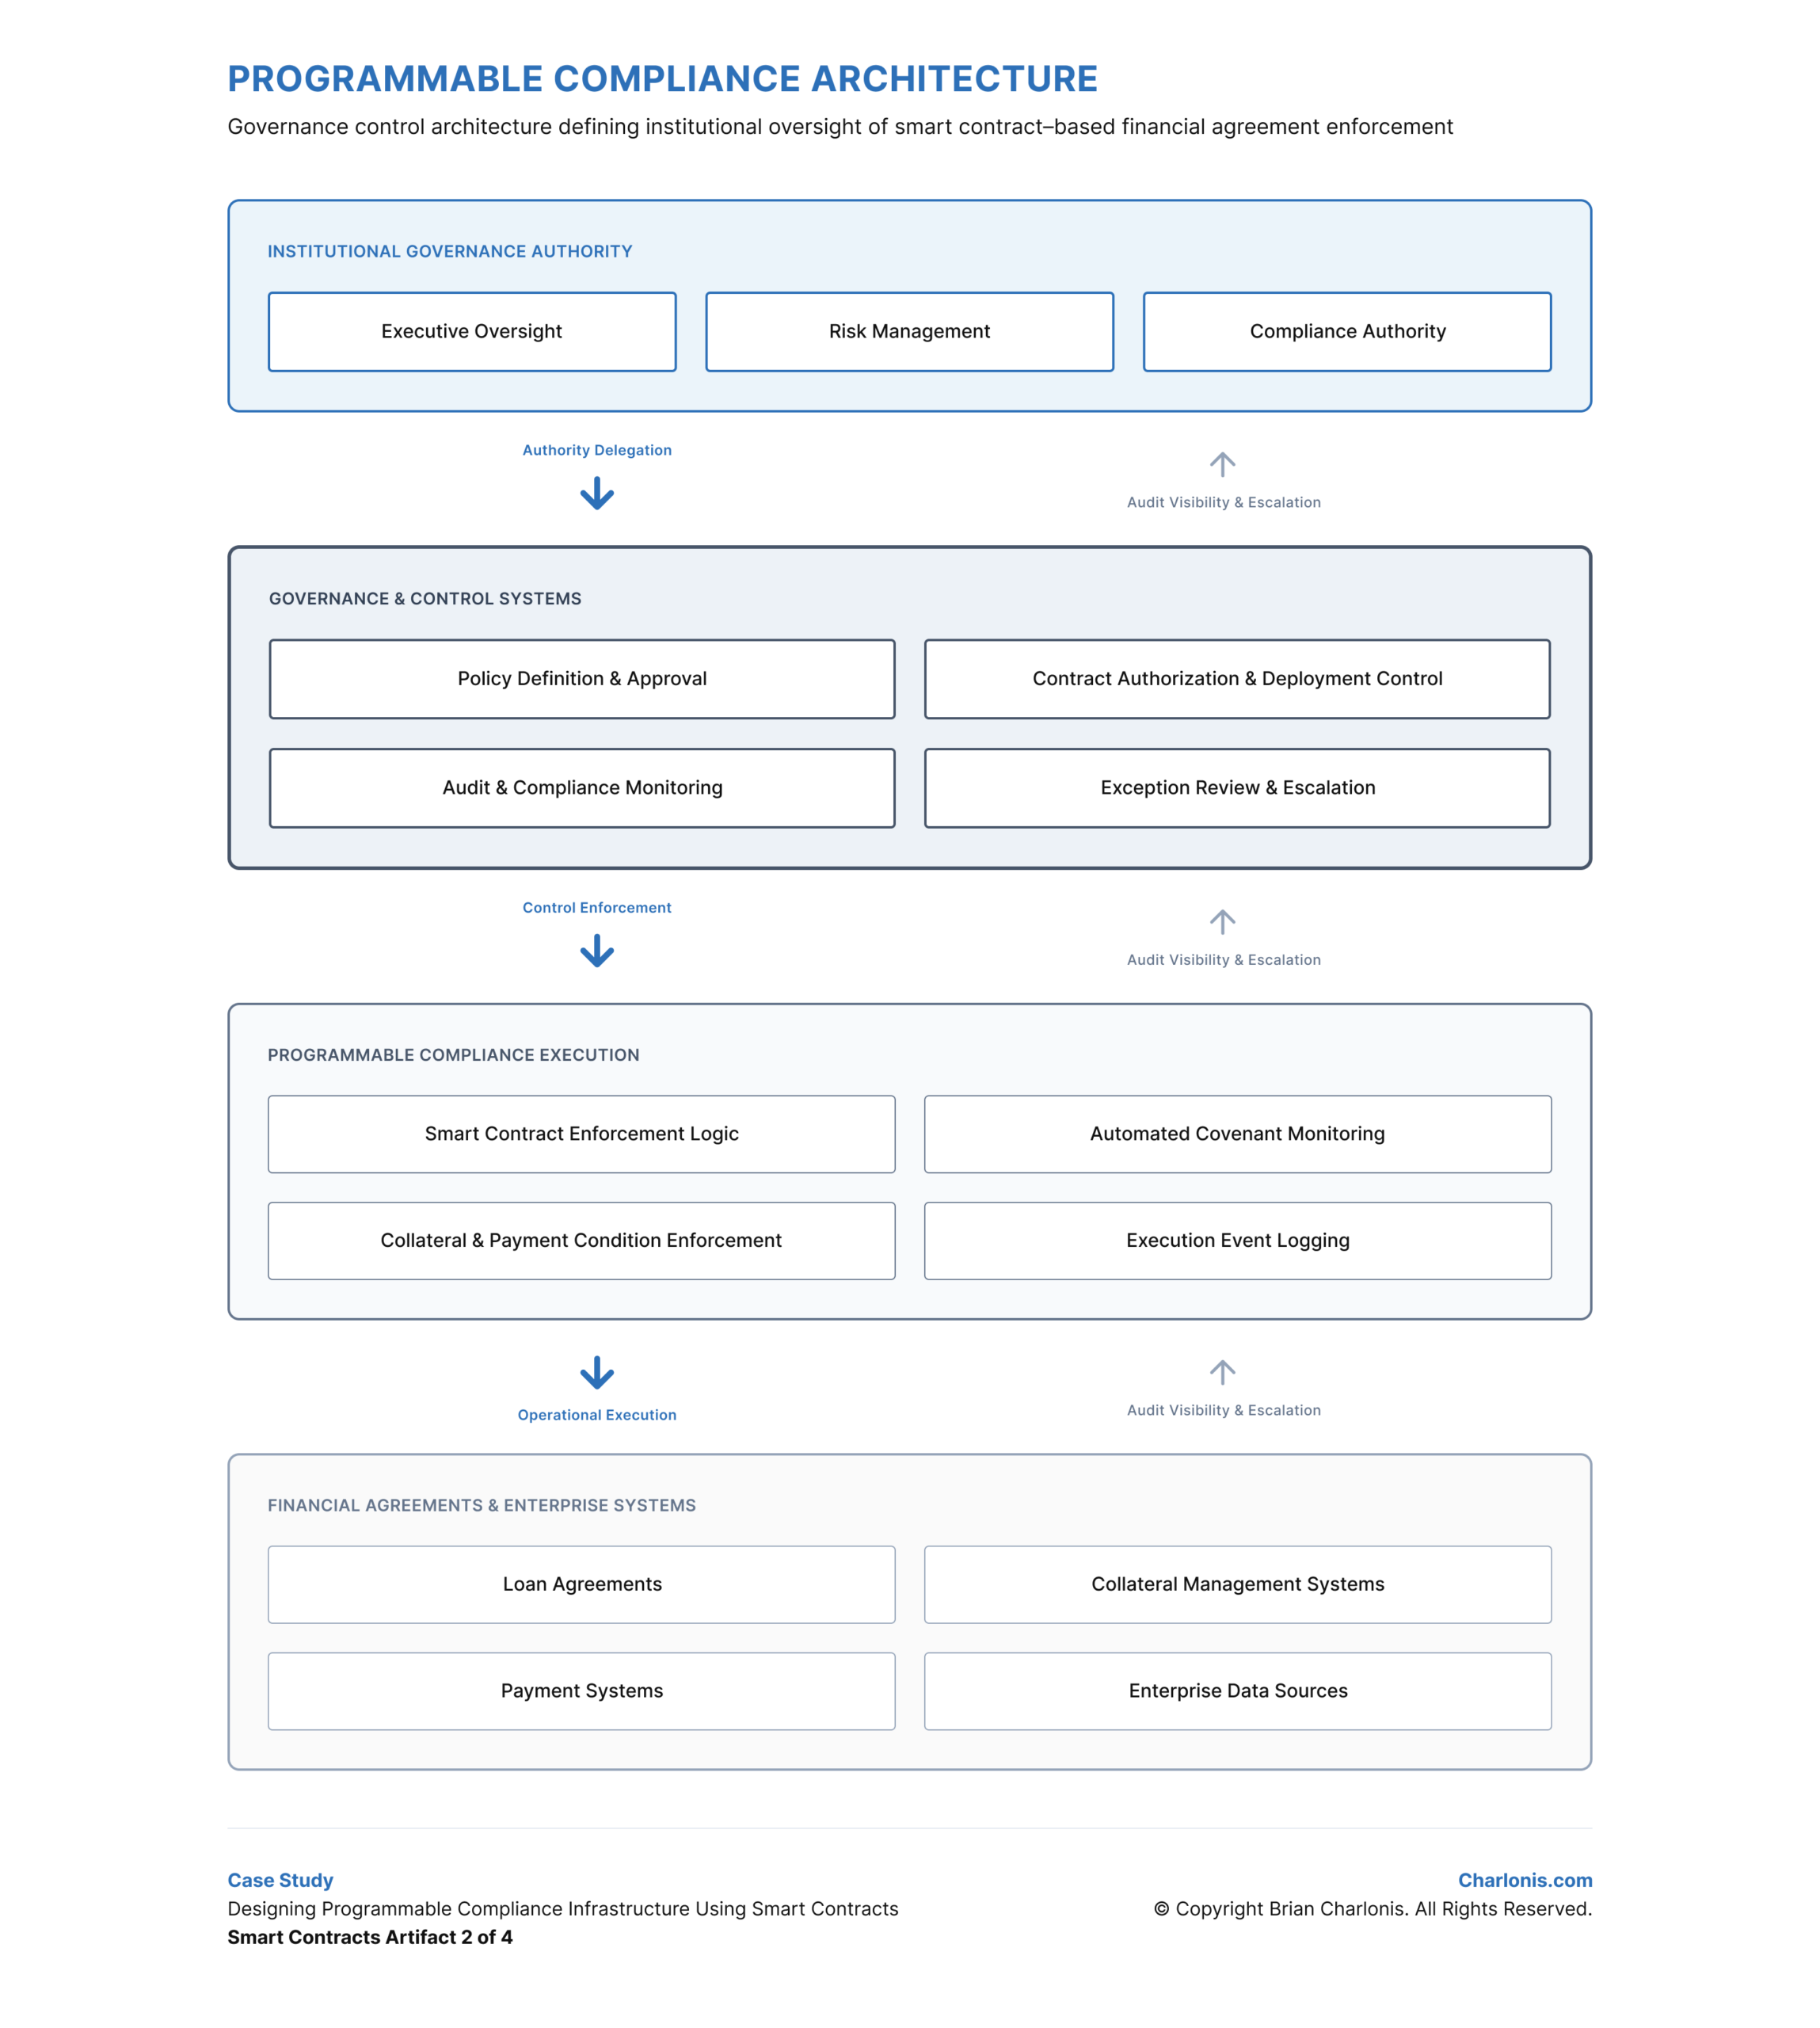
Programmable Compliance Operating Model
The operating model positioned smart contracts as programmable compliance infrastructure under institutional authority, compliance control, audit visibility, escalation pathways, and executive oversight. It clarified how deterministic execution could be evaluated without treating automation as a substitute for accountability.
Key Elements
- Layered governance architecture for programmable compliance.
- Institutional authority over automated financial agreement behavior.
- Compliance control integration.
- Audit visibility requirements.
- Escalation pathway alignment and executive oversight expectations.
Artifact type: Operating model / governance architecture.
The artifact positioned smart contracts under institutional authority, compliance control, audit visibility, and governance oversight rather than as autonomous technical systems.
How It Shaped Decisions
This component would support governance, compliance, audit, enterprise architecture, and executive leadership stakeholders in determining how programmable compliance should fit within institutional control frameworks, which oversight mechanisms were required, and how automated execution could remain accountable.
Execution Authority and Escalation Model
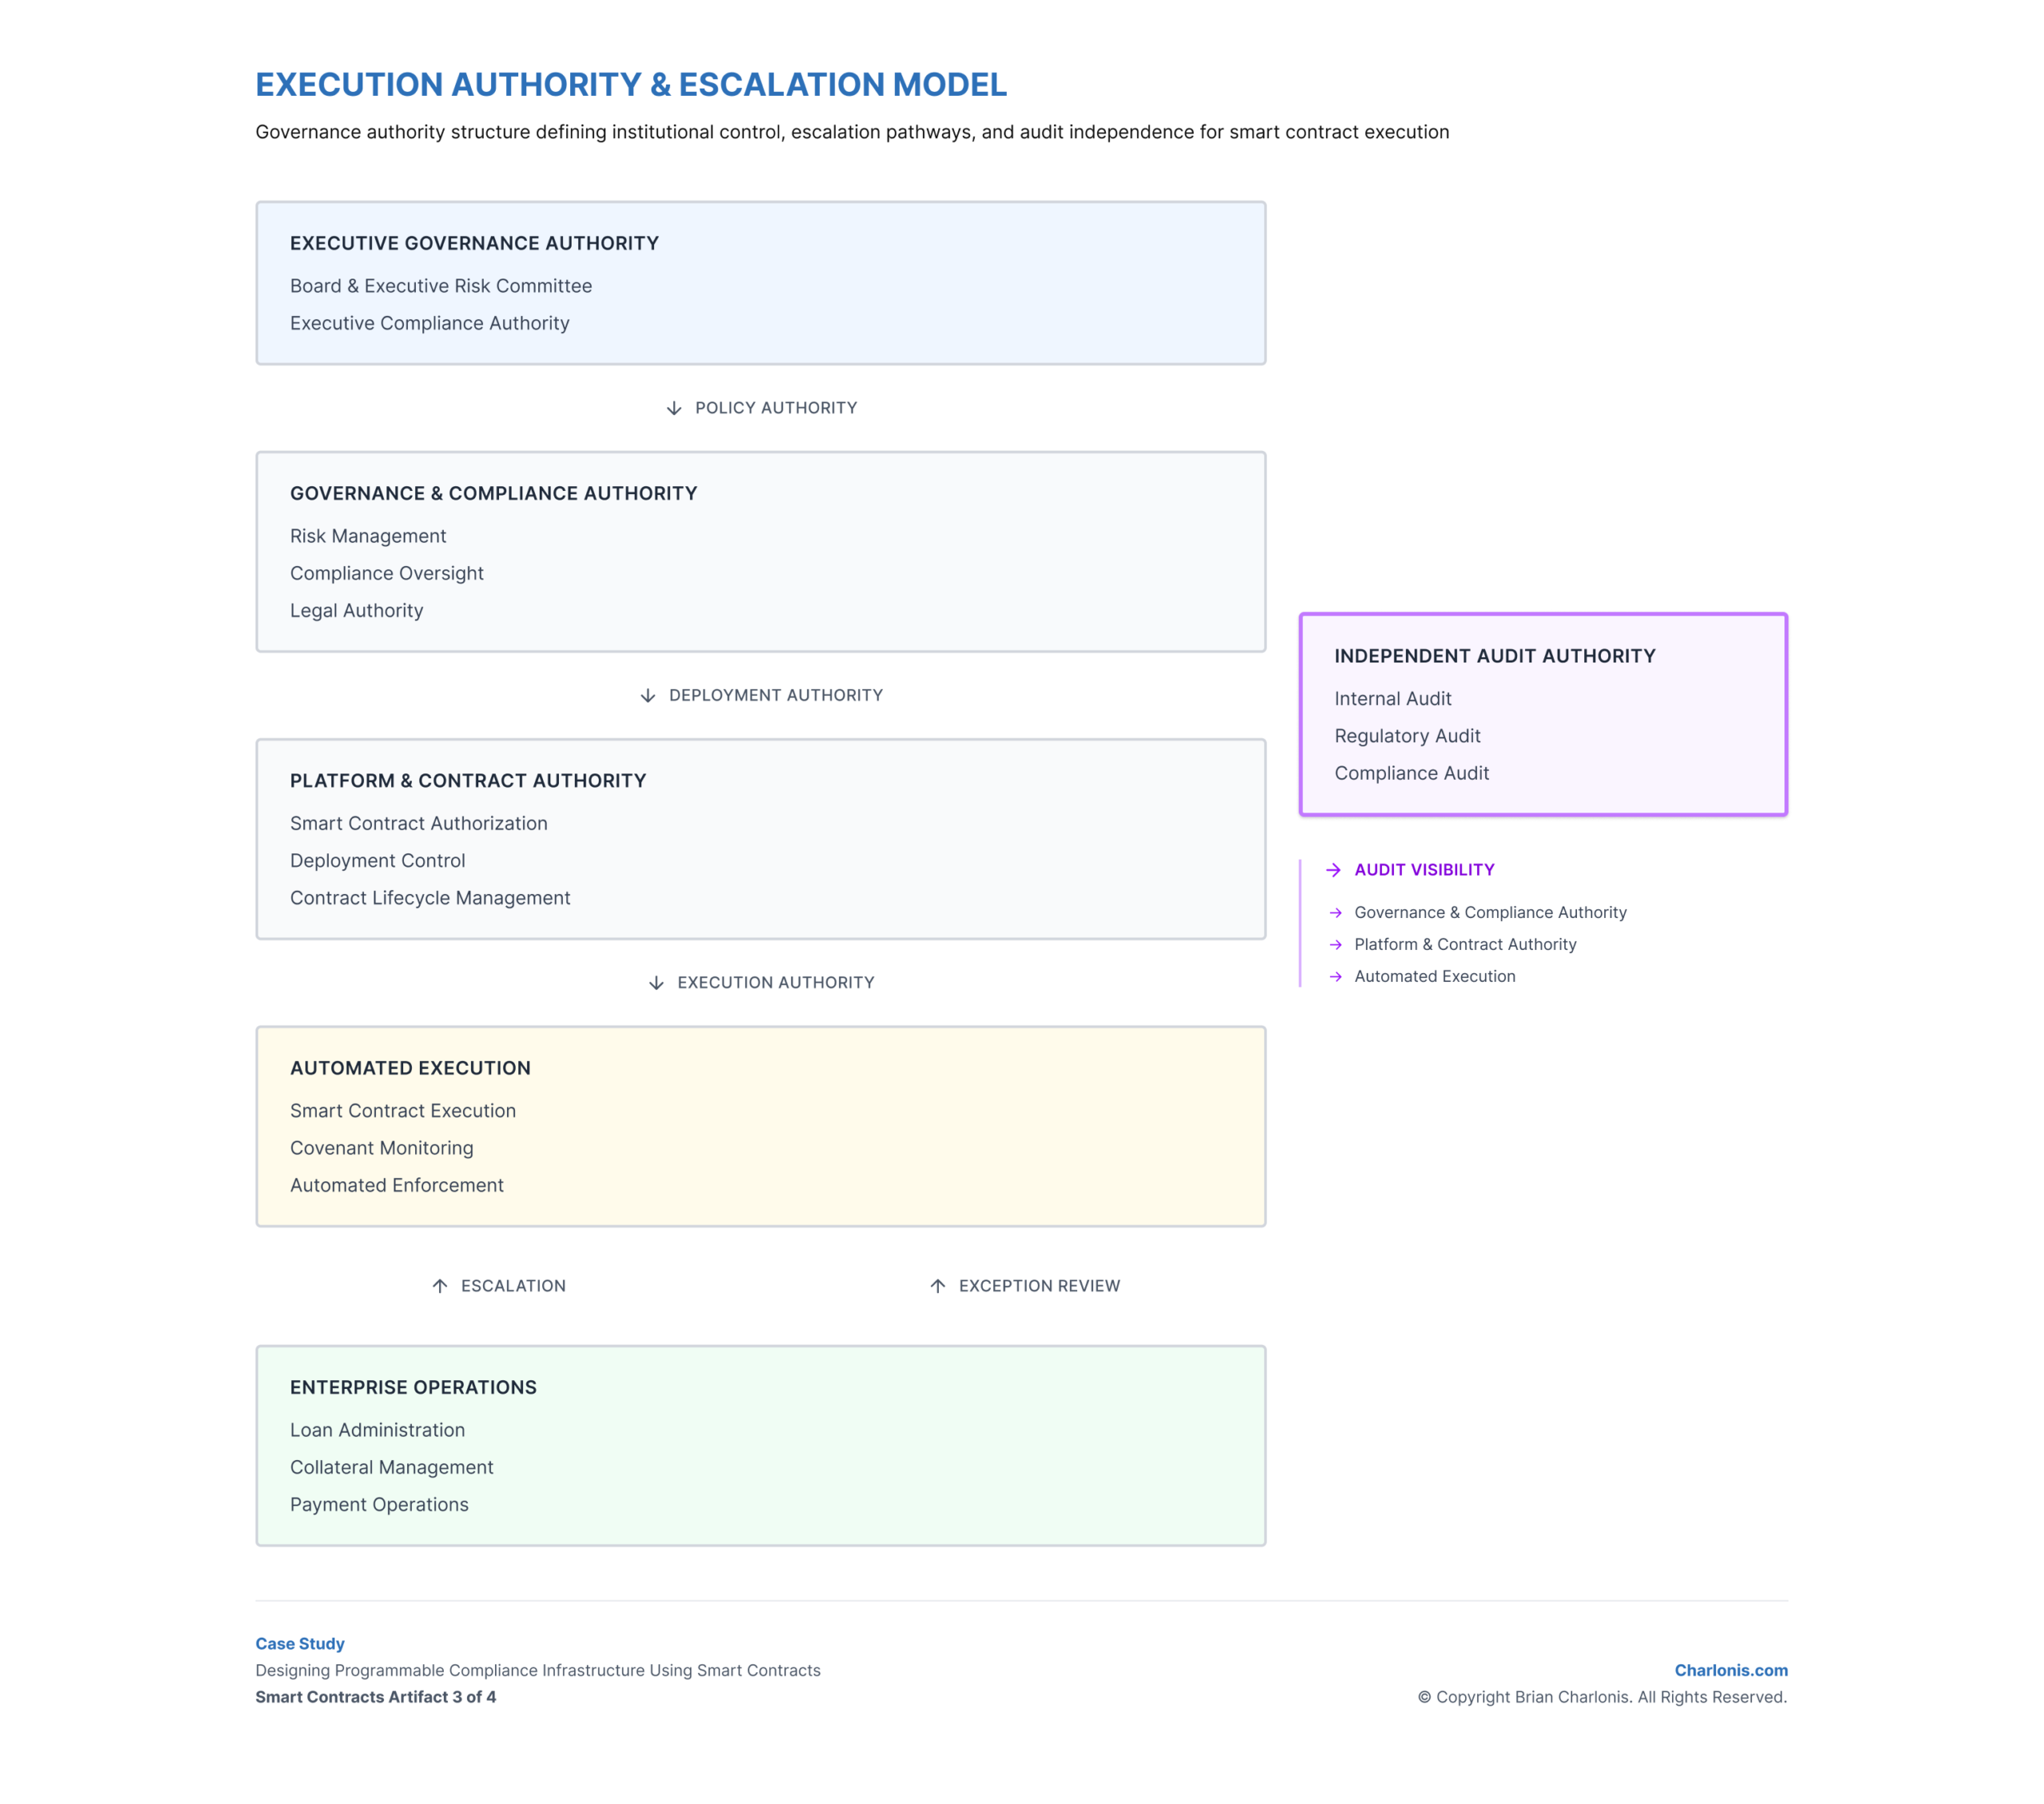
The authority and escalation model defined who could authorize, activate, pause, override, intervene in, escalate, or change smart-contract-based execution. It clarified that automated financial agreement behavior should not advance unless institutional intervention capability and separation of duties were defined.
Key Elements
- Authority delegation across governance and execution layers.
- Separation of duties across authorization, deployment, execution, and audit.
- Activation controls for programmable contract behavior.
- Pause, override, and intervention capability.
- Escalation pathways for exceptions, breaches, or disputed execution events.
Artifact type: Authority model / escalation framework.
The artifact connected authority delegation, separation of duties, activation controls, intervention rights, escalation pathways, and audit independence across governance and execution layers.
How It Shaped Decisions
This component would support governance, compliance, audit, platform, and enterprise architecture stakeholders in determining who could authorize contract behavior, who could activate or pause execution, how exceptions should escalate, and how separation of duties should preserve institutional control and audit independence.
On-Chain and Off-Chain Responsibility Framework
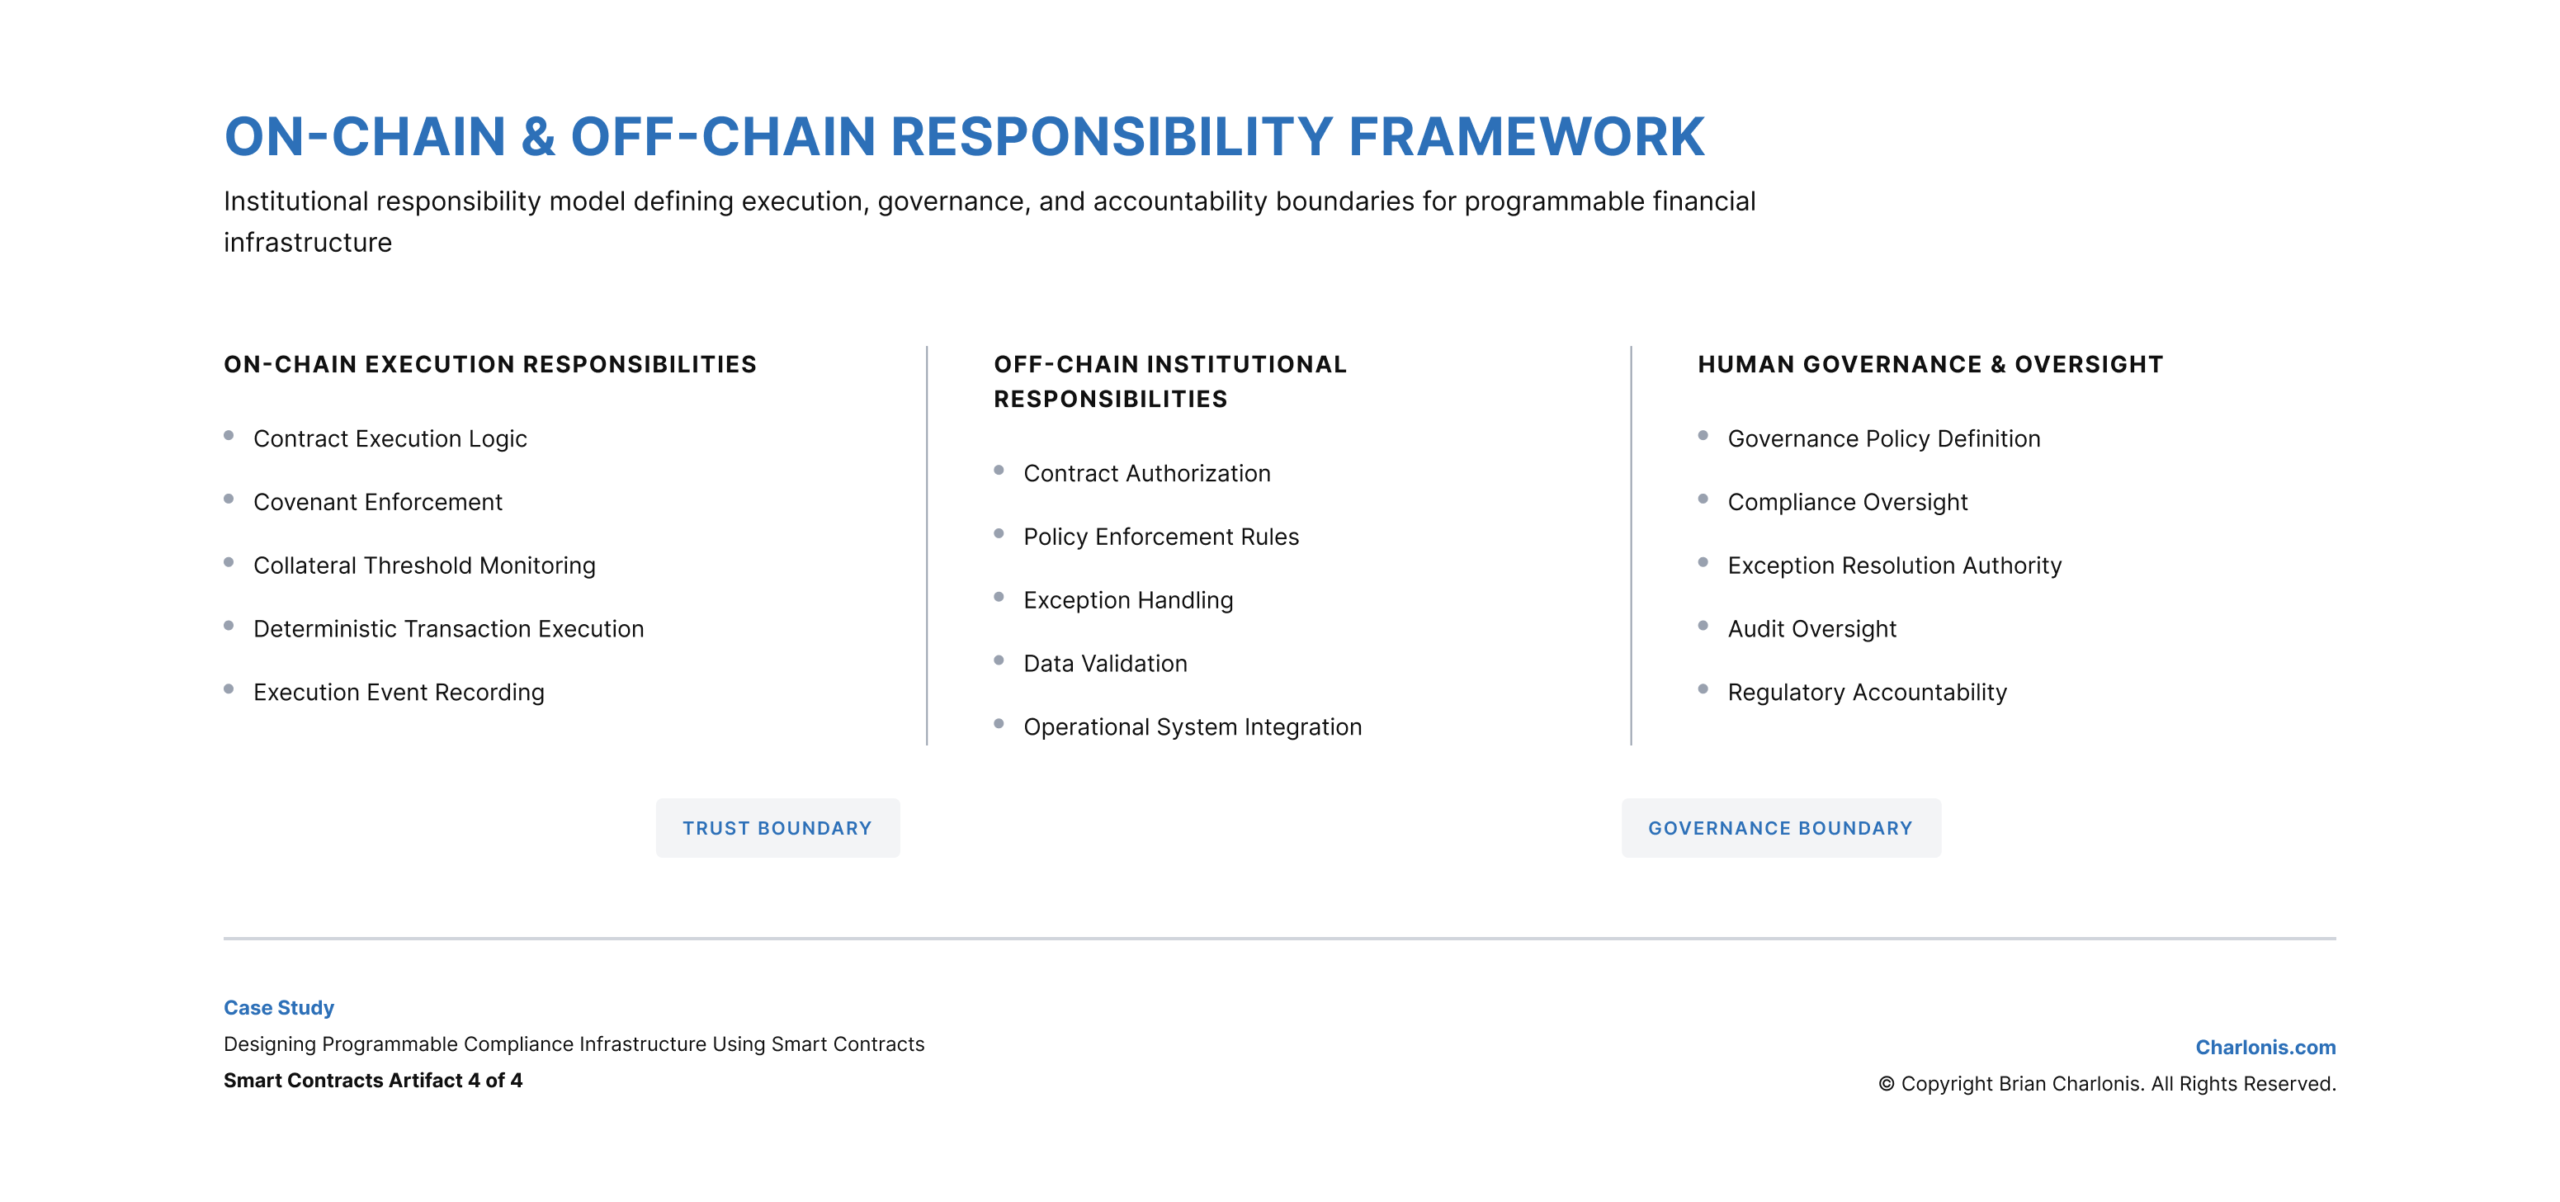
The responsibility framework clarified accountability across programmable execution, institutional systems, off-chain data sources, and human governance. It defined which responsibilities could be supported by automated execution and which could not be delegated to code.
Key Elements
- Responsibility boundaries across on-chain execution.
- Responsibility boundaries across off-chain systems and institutional data sources.
- Human governance ownership for approval, intervention, and review.
- Accountability mapping across automated and manual control points.
- Audit evidence expectations across execution layers.
Artifact type: Responsibility framework / accountability model.
The artifact mapped accountability across programmable execution, institutional systems, human governance, audit evidence, and regulatory accountability expectations.
How It Shaped Decisions
This component would support enterprise architecture, regulatory, governance, compliance, and audit stakeholders in determining where accountability should sit across execution layers, which responsibilities could not be delegated to code, and what evidence was required to support audit, review, and regulatory accountability.
TRADEOFFS & DECISIONS
Lifecycle Discipline vs Deployment Flexibility
- Tradeoff: Strong lifecycle governance could strengthen institutional control, but would increase the work required before deployment feasibility could advance.
- Response: I defined governance checkpoints across creation, approval, deployment, execution, monitoring, upgrade, and retirement before smart-contract-based execution could be evaluated for deployment.
Automation vs Institutional Authority
- Tradeoff: Programmable compliance could improve consistency, but automation could not replace institutional authority.
- Response: I positioned smart contracts under institutional governance, compliance control, audit visibility, escalation pathways, and executive oversight.
Execution Speed vs Intervention Control
- Tradeoff: Deterministic execution could reduce manual delay, but speed created risk if pause, override, escalation, or intervention rights were unclear.
- Response: I defined authority delegation, separation of duties, activation controls, escalation pathways, and intervention capability before execution approval could be considered.
Automation vs Accountability Boundaries
- Tradeoff: Smart contracts could automate parts of financial agreement behavior, but accountability still needed to span code, data, institutional systems, and human governance.
- Response: I mapped responsibility boundaries across on-chain execution, off-chain systems, and human decision authority.
OUTCOMES
This case produced a programmable compliance governance architecture, four conceptual artifacts, lifecycle-control logic, authority-delegation model, escalation and intervention requirements, audit-visibility structure, and responsibility-boundary framework. It was developed as an independent conceptual transformation scenario and does not claim production smart-contract deployment, institutional adoption, regulatory approval, smart contract audit authority, technical architecture ownership, measured automation improvement, or long-term infrastructure operations.
Impact Summary
- Created a governance architecture for evaluating smart-contract-based compliance execution.
- Defined how programmable financial agreement behavior could remain subject to lifecycle control.
- Positioned programmable compliance under institutional authority, governance control, and audit oversight.
- Clarified authority, escalation, and intervention requirements before deployment consideration.
- Mapped accountability across on-chain execution, off-chain systems, and human governance.
Evidence
- Smart Contract Governance Lifecycle defined lifecycle governance across contract creation, approval, deployment, execution, monitoring, upgrade, change control, retirement, and decommissioning.
- Programmable Compliance Operating Model positioned smart contracts under institutional authority, compliance control, audit visibility, and governance oversight.
- Execution Authority and Escalation Model defined authority delegation, separation of duties, activation controls, intervention rights, and escalation pathways across governance and execution layers.
- On-Chain and Off-Chain Responsibility Framework defined responsibility boundaries across programmable execution, institutional systems, human governance, audit evidence, and regulatory accountability expectations.
- The model translated smart contract execution mechanics into governance control requirements.
- The model clarified that programmable execution should remain subject to institutional intervention capability and human authority.
Signals Monitored
- Governance lifecycle completeness across creation, approval, deployment, execution, monitoring, upgrade, and retirement.
- Authority delegation clarity, separation-of-duties coverage, escalation readiness, and intervention control.
- Audit visibility across lifecycle events, execution behavior, approvals, changes, and interventions.
- Responsibility-boundary clarity across on-chain execution, off-chain systems, institutional data, and human governance.
Decision Thresholds
- Permit programmable execution only under defined governance authority and lifecycle approval.
- Require institutional intervention capability before automated enforcement or deterministic execution advances.
- Require responsibility boundaries that preserve accountability across on-chain execution, off-chain systems, and human governance.
- Require audit visibility and alignment with existing institutional control frameworks before deployment feasibility is considered.
Brian completed the smart contract governance lifecycle, programmable compliance operating model, execution authority and escalation model, on-chain and off-chain responsibility framework, and decision logic that could support stakeholder review and deployment-feasibility evaluation. Production implementation, smart contract audit authority, regulatory approval, technical architecture ownership, deployed smart-contract systems, institutional adoption, measured automation outcomes, and long-term infrastructure operations remained outside the scope of the case.
LEADERSHIP REFLECTION
What This Case Demonstrates
- Programmable execution does not reduce governance requirements. It increases the need for explicit authority, lifecycle, escalation, and responsibility design.
- Smart contracts must operate as institutional infrastructure under governance authority, not as autonomous technical systems outside accountability.
- Separation of duties across authorization, deployment, execution, and audit layers is essential for regulatory trust.
- Governance architecture determines deployment feasibility more than technical capability in regulated environments.
What I Would Validate Next
- Regulator-facing expectations for lifecycle governance before deployment-feasibility evaluation.
- Testing and validation requirements for deterministic execution logic.
- Intervention mechanisms under simulated breach or disputed-execution scenarios.
- Audit evidence requirements across on-chain execution, off-chain systems, and human governance.
What I Would Watch Closely
- Programmable compliance being treated as automation rather than governed infrastructure.
- Contract logic advancing before lifecycle governance is defined.
- Technical feasibility being mistaken for institutional deployment readiness.
The central challenge was not whether smart contracts could automate financial agreement behavior.
It was whether programmable execution could operate inside lifecycle governance, institutional authority, escalation controls, audit visibility, and responsibility boundaries before deployment feasibility could be justified.
RECOMMENDED
CASE STUDY
BLOCKCHAIN INFRASTRUCTURE
Testing Smart Contracts to Understand Trust, Risk, & Governance
Built and operated private Ethereum environments, created genesis blocks, mined native ETH, deployed Solidity contracts, tested transaction execution, observed gas behavior and state changes, and translated hands-on execution testing into trust-boundary, product, risk, and governance judgment.
Smart Contracts
Blockchain Infrastructure
Execution Literacy

CASE STUDY
MONITORED AUTONOMY
Agentic AI Systems for Enterprise Regulatory & Risk Intelligence
Designed a monitored-autonomy model for agentic regulatory intelligence, defining how regulatory signals would be classified, routed, monitored, contained, escalated, and translated into executive decision support for high-risk enterprise workflows.
Agentic AI
Regulatory Intelligence
Monitored Autonomy
CASE STUDY
DATA & RESPONSIBLE AI GOVERNANCE
Operationalizing Data & Responsible AI Governance Across a Global Enterprise
Defined a Data and Responsible AI Governance operating model connecting risk-tiered intake, accountable business ownership, cross-functional controls, lifecycle oversight, reassessment, and executive visibility without routing every AI decision through one centralized approval bottleneck.
Data & Responsible AI Governance
Lifecycle Governance
Decision Rights

CASE STUDY
INSTITUTIONAL GOVERNANCE
Enterprise Governance & Policy Architecture for AI Systems
Defined an enterprise AI governance architecture with an AI charter, portfolio risk taxonomy, capital-allocation governance model, and vendor governance framework to clarify oversight, decision authority, policy expectations, and investment discipline for responsible AI scale.
AI Governance
Enterprise Decision Systems
Capital Discipline
Trust is an architectural discipline.
If you are governing AI, programmable infrastructure or emerging financial systems in regulated environments, let’s connect on LinkedIn.